
From the Cybr blog
Ethical Hacking
Read practical guides, tutorials, and security research about Ethical Hacking from the Cybr blog.
Browse the archive
More Ethical Hacking articles
Useful IP widget for CTFs
Who can’t use more convenience? If you’re familiar with VPN profiles when it comes to CTF programs like THM and HTB, I’m sure you’ve forgotten…
Read article
How a pentester struggled with bug bounties until this new mindset helped him breakthrough
“It was a long, arduous, journey to finding my first bug.” Then one day, Hakluke attended a talk by @shubs that changed his mindset about how to approach bug bounties and helped him breakthrough in finding his first bugs.
Read articleWhat you need before submitting a bug bounty report
I’m writing this because I’ve been seeing people struggle to understand when they’re ready to submit a bug report. Maybe they find something interesting as…
Read article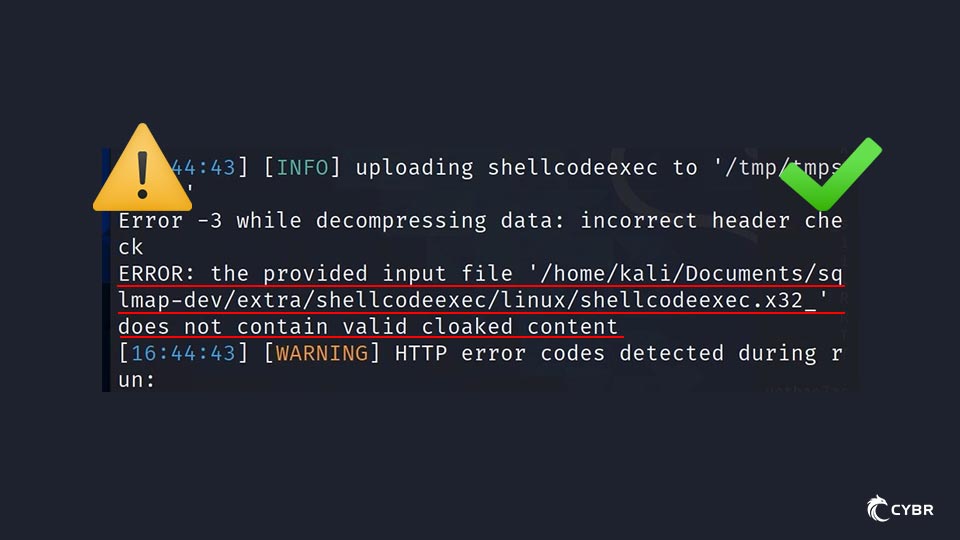
How to fix ‘does not contain valid cloaked content ‘ in sqlmap
While working through my Practical Guide to sqlmap for SQL Injections course, I ran into an issue with sqlmap’s included shellcodeexec. There was an error…
Read articleNew course: The Practical Guide to sqlmap for SQL Injection
Ever since launching our Injection Attacks: The Free Guide course, we’ve received numerous requests to continue building SQL injection-related content, including how to use the…
Read article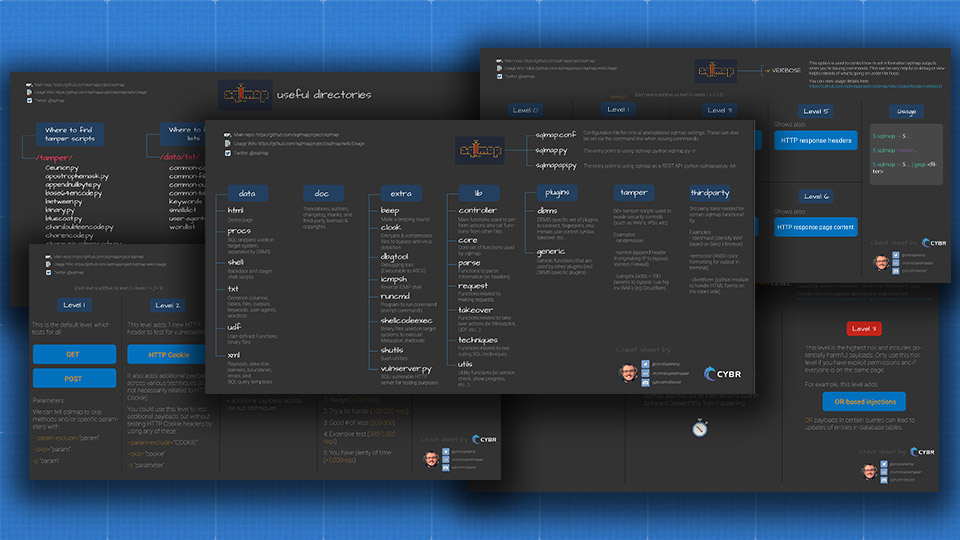
6 sqlmap cheat sheets to help you find SQL injections
Here’s a collection of cheat sheets we created to go along with our course: The Practical Guide to sqlmap for SQL Injection. If you find…
Read article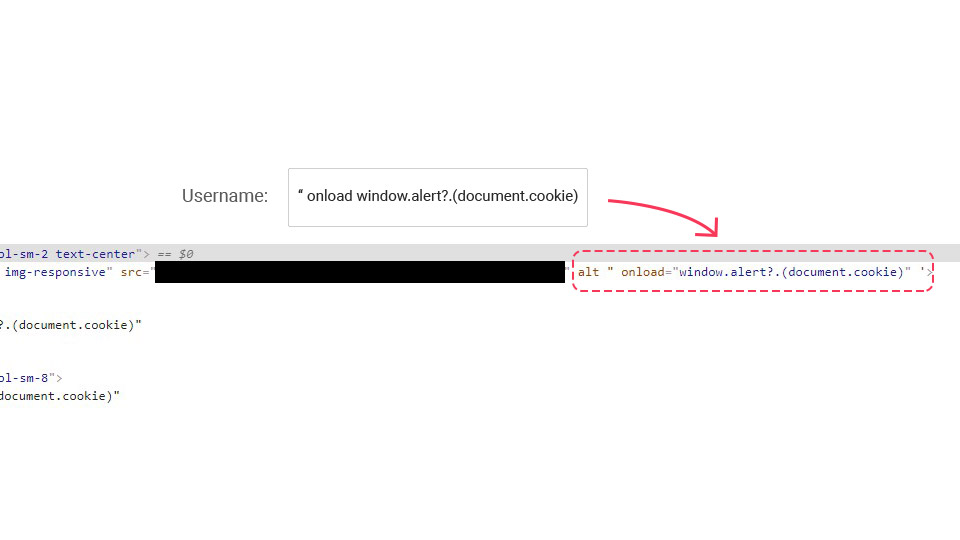
Stored XSS vulnerability in image alt attribute to steal cookies (Bug Bounty)
I recently found a stored XSS vulnerability through an image alt attribute. While I can’t share any details about where, I can share details about…
Read article
New Course: Beginner’s Guide to sqlmap
One of our most popular and requested content categories has been regarding SQL injections and the popular tool sqlmap that is used to help find…
Read articleCybr’s Injection Attacks Course Badge Gets Added to NYU Cyber Fellows Program
In addition to our Introduction to Application Security and Cross-Site Scripting badges, we are officially announcing the addition of the Injection Attacks badge to the…
Read article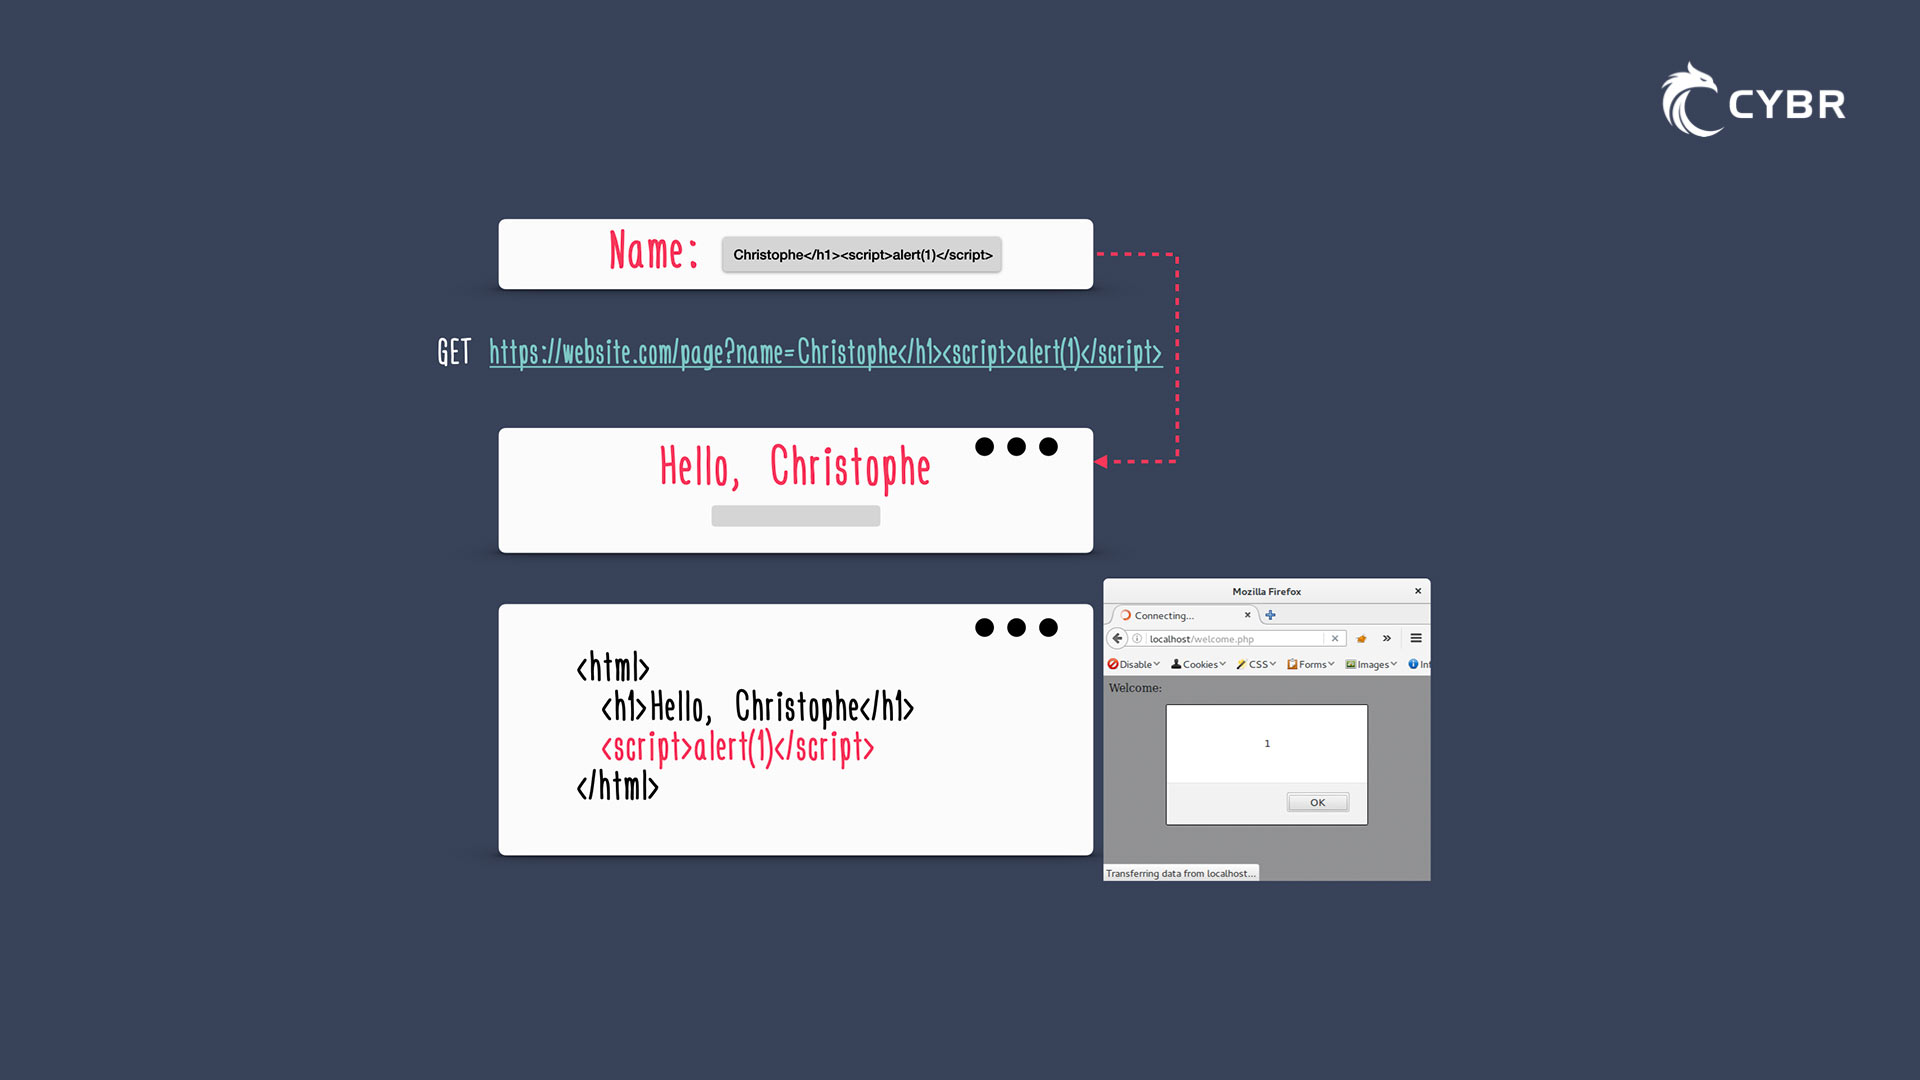
What is Cross-Site Scripting (XSS)?
According to both OWASP and CWE, Cross-Site Scripting is one of the top 10 most dangerous web application security risks, and for good reason: OWASP’s…
Read article