
From the Cybr blog
Ethical Hacking
Read practical guides, tutorials, and security research about Ethical Hacking from the Cybr blog.
Browse the archive
Latest articles
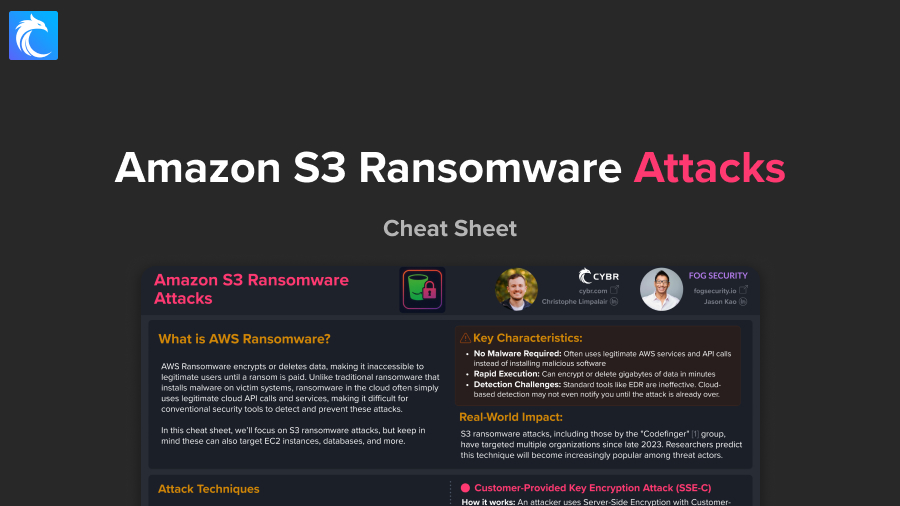
Amazon S3 Ransomware Attacks [Cheat Sheet]
In this cheat sheet, we break down a growing threat: Amazon S3 ransomware attacks.
Read article
How hackers use this AWS ransomware attack
There’s a “new” ransomware attack being used in AWS that you need to know about. But what is it, how does it work, and how can you defend against it? Let’s find out.
Read article
AWS IAM Privilege Escalation Learning Path
So you want to learn about AWS IAM privilege escalations…where should you start, and what should you learn? We launched a course specifically for this…
Read article
AWS Secrets Manager Enumeration – Cybr Lab Walkthrough
In this lab walkthrough, we’re going to take a look at how to enumerate the AWS Secrets Manager service in order to better understand how…
Read article
Introducing Free AWS Cloud Security Hands-On Labs
Our free Hands-On Labs are a great way to dip your toes into the AWS cloud security space completely risk-free. No credit card required, just…
Read articleRequest forgeries (CSRF, XSRF, SSRF)
In 2020, CheckPoint Research announced multiple vulnerabilities in the popular social media application named TikTok. One of the found vulnerabilities allowed an attacker to delete…
Read article
Intro to AWS Pentesting (with Pacu)
In this article, you’re going to learn how to hack AWS cloud environments so that you can find exploitable vulnerabilities in your own AWS accounts…
Read article
Exercise types (red/blue/white/purple teams)
We’ve talked about how we can use vulnerability scans, penetration tests, and bug bounties to find vulnerabilities in our systems. Another approach you may have…
Read articleWhat are SQL Injections? // Explained in 180 seconds
Whenever you visit a website or use some kind of application, that website or app needs to pull data from a database. For example, let’s…
Read articleImportant pentesting concepts for the Security+
You’ve been running vulnerability scans on a regular basis, you’ve expanded that into a broader vulnerability assessment approach, and you’ve been fixing everything that’s been…
Read article