
From the Cybr blog
Christophe
Read articles by Christophe from the Cybr blog.
Browse the archive
More Christophe articles
Bluesnarfing and Bluejacking
Studying for the Security+ exam? Here’s a quick and easy read for a topic covered in the exam objectives. What is bluesnarfing? If you were…
Read article
Biometrics techniques and concepts for authentication
We talked about how biometrics can be used for multifactor authentication in order to verify someone’s identity. Biometric authentication refers to something you are (as…
Read articleKey stretching concepts and algorithms
One of the best ways to make a password strong is to make it long. The longer the password is, the harder it is to…
Read articleHashing use cases
In practice, what is hashing used for? How is it being used in the real world? Let’s take a look at a few common hashing…
Read articleHash Tables, Rainbow Table Attacks, and Salts
As we talked about, applications that properly handle passwords don’t actually store the passwords themselves in databases, but instead, store hashes of passwords. That’s why…
Read article
Multifactor authentication (MFA) factors and attributes
Password-based authentication has been proven time and time again to be a vulnerable form of authentication. One of the best defenses is using Multifactor Authentication,…
Read articleEncrypted versus hashed passwords. What’s the difference?
As you study for the CompTIA Security+ exam, it’s important that you understand the differences between plaintext, encrypted, and hashed passwords. It’s common to hear…
Read article
What to know about vulnerability scans for the Security+ exam
Regularly auditing systems for potential vulnerabilities is an important part of securing an organization’s environments, systems, and applications. One of the ways that we can…
Read article
Ultimate Study Guide for the CompTIA Security+ (SY0-601)
Preparing for certification exams can be stressful when you’re not sure what to expect or what to study. It doesn’t help when information that can…
Read article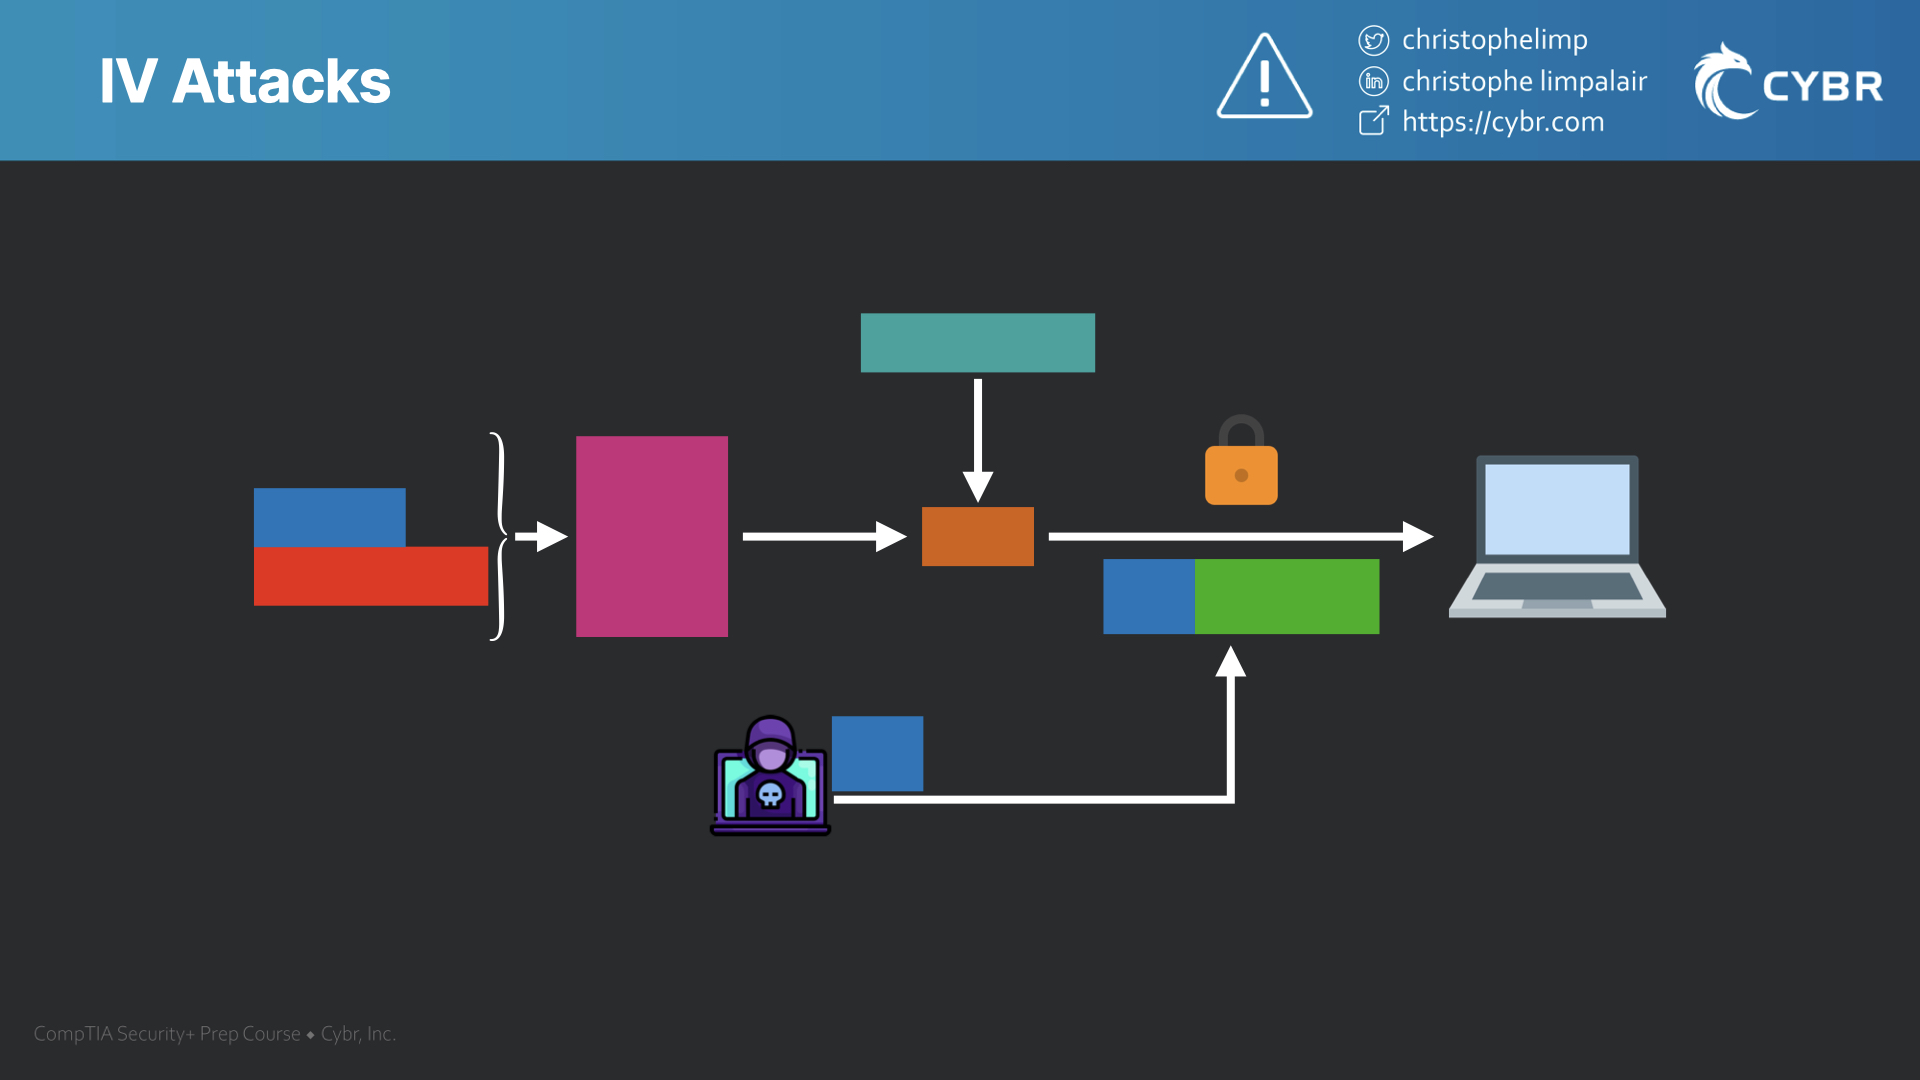
Initialization Vector (IV) attacks with WEP
Understanding Initialization Vector (IV) attacks is important for the CompTIA Security+ exam, but it can be confusing if you’re not as familiar with cryptography concepts.…
Read article