
Section 2 · Infrastructure Security Free preview
VPC networks
Access the interactive diagram for this lesson here. (It may ask you to create a free account in order to view. You do not need paid features to view this course’s content so you can ignore that!)
When it comes to infrastructure security in the AWS cloud, one of the core components to understand is the Amazon VPC, or Virtual Private Cloud.
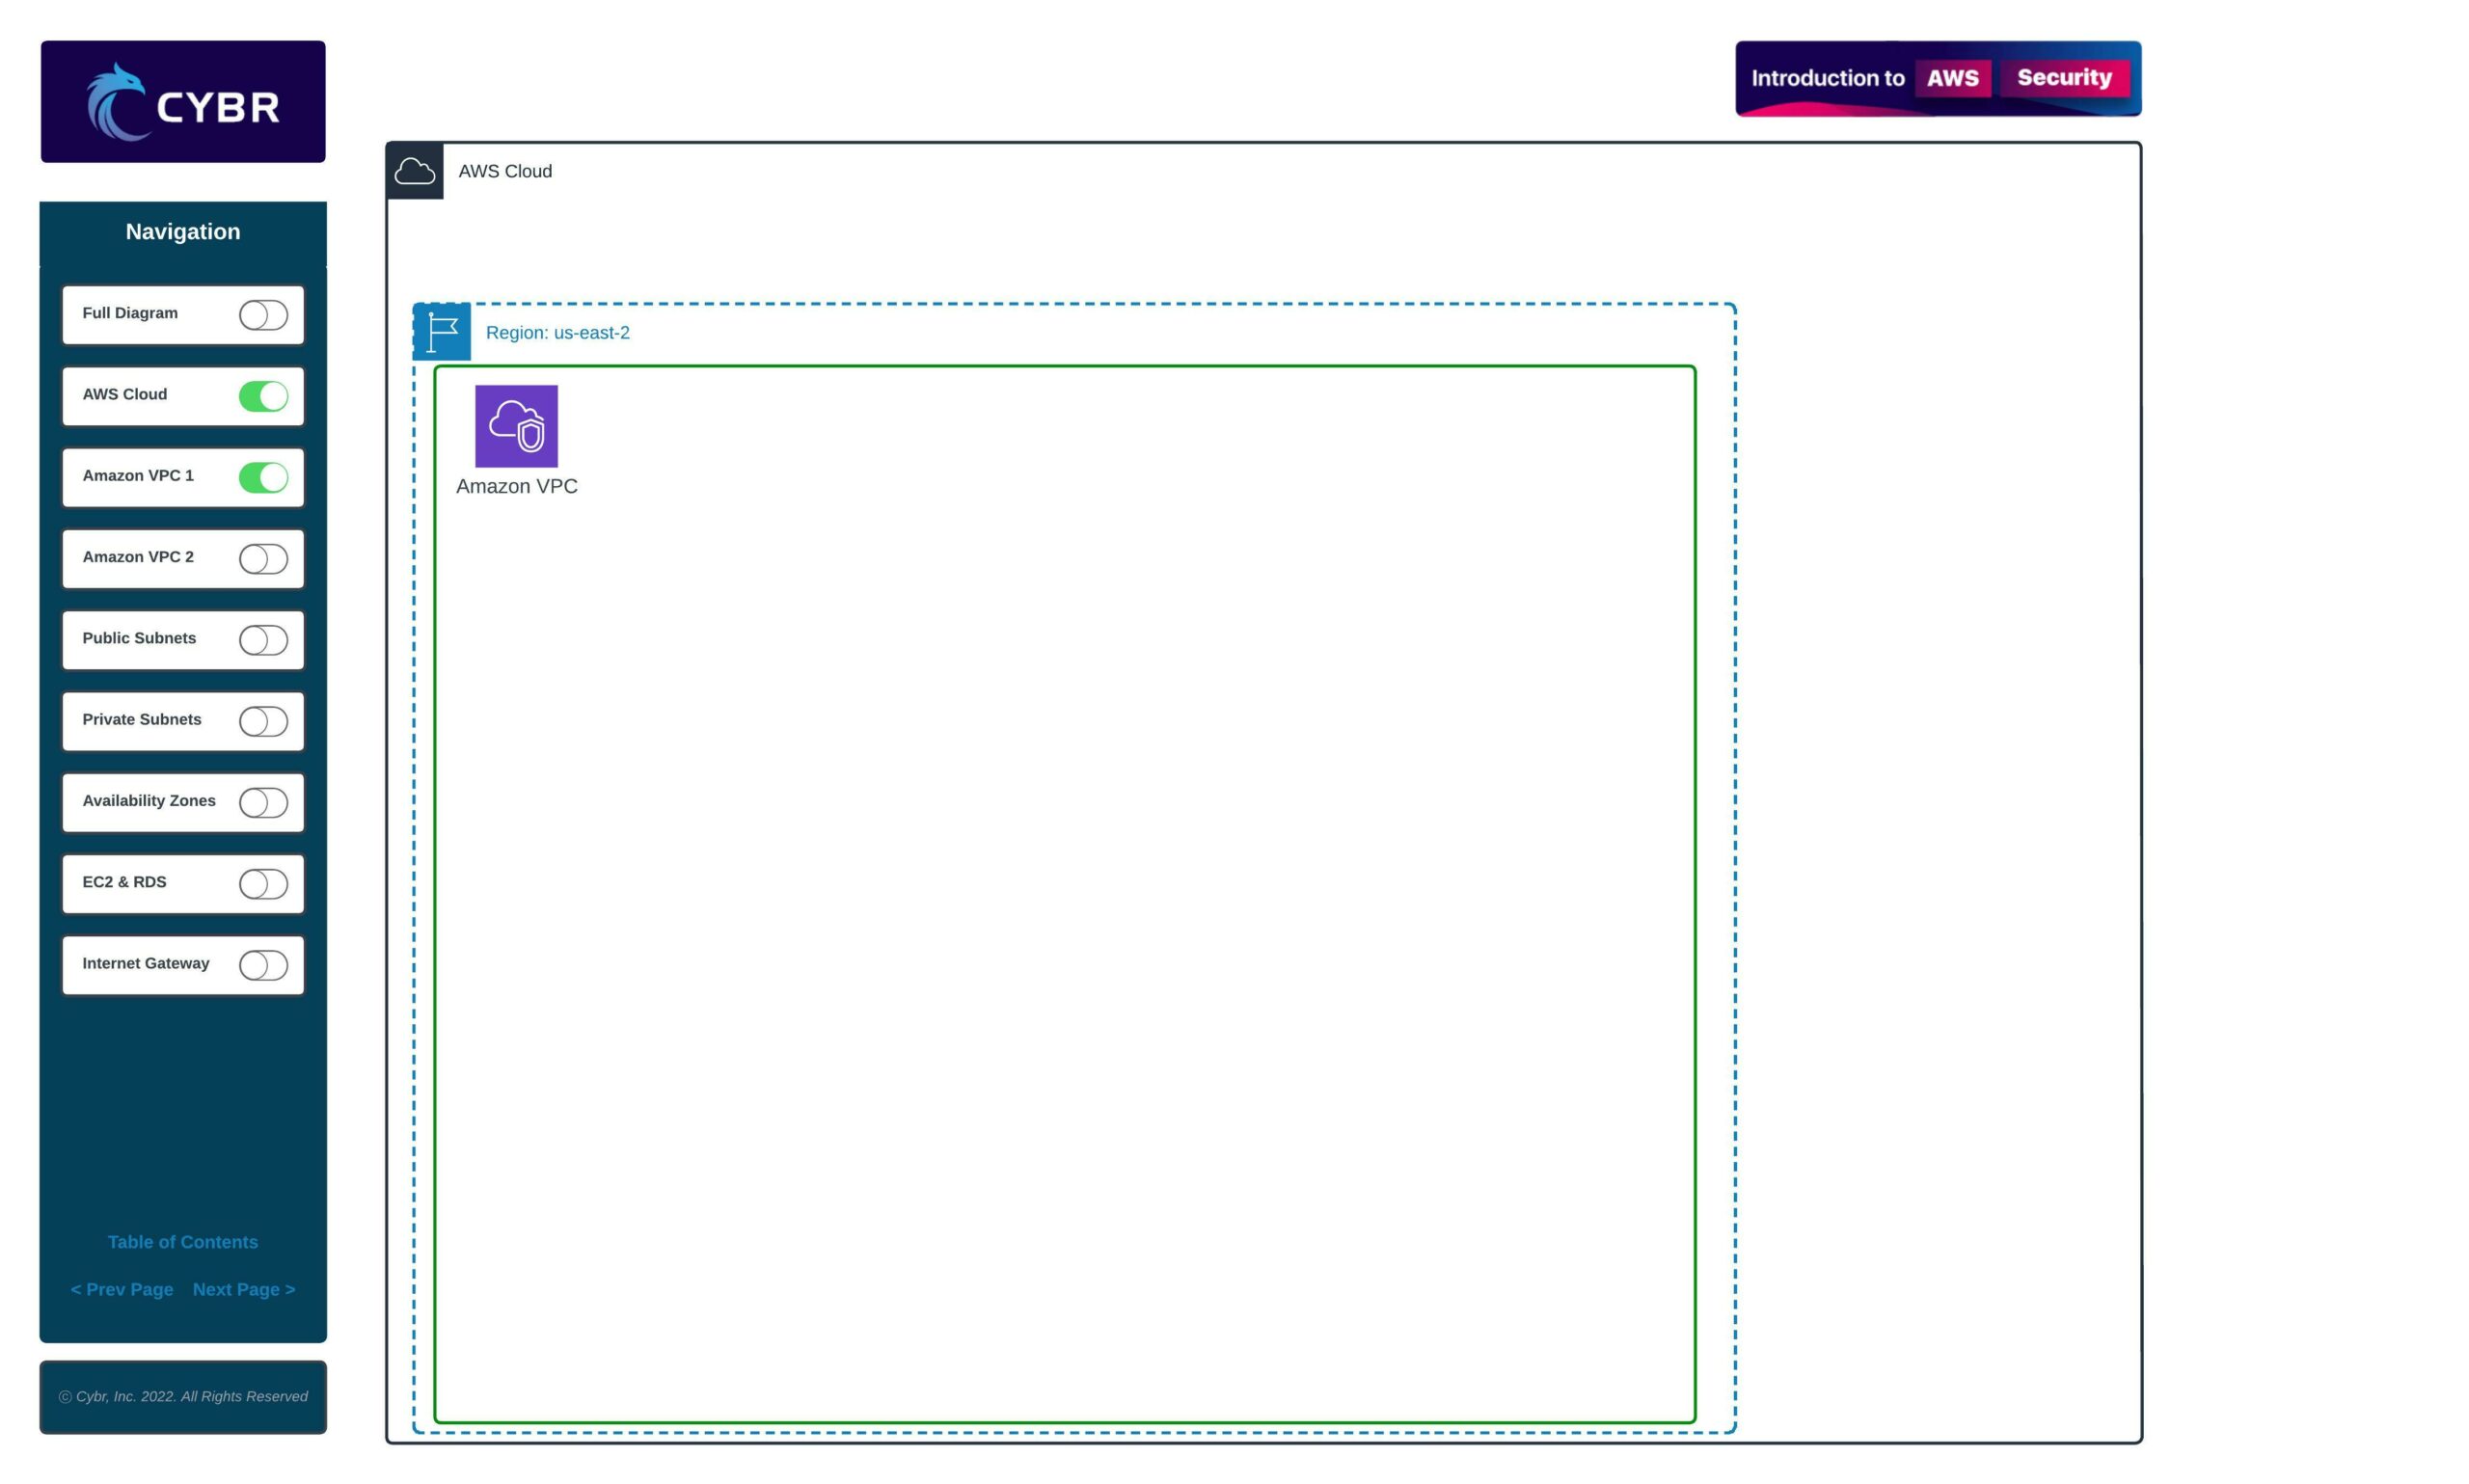
The Amazon VPC is the basic building block in AWS, and it’s represented by the green rectangle in our sample architecture. Just like we can create virtual networks on-premises, we can also create virtual networks in the cloud.
These VPCs let you carve out a section of the cloud where you can then launch your own resources. Once created, no one else can use that section apart from you, and you can launch all kinds of resources like: web servers, app servers, databases, and so on…
You can create multiple of these virtual networks, and you can either keep them in isolation, or you can connect them to other virtual networks, and even to on-premises resources.
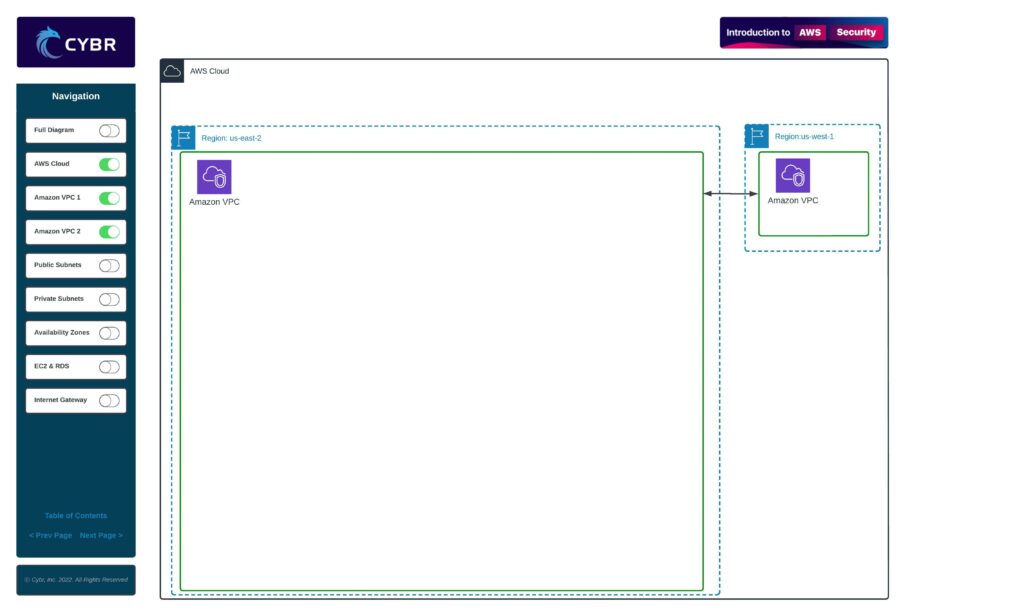
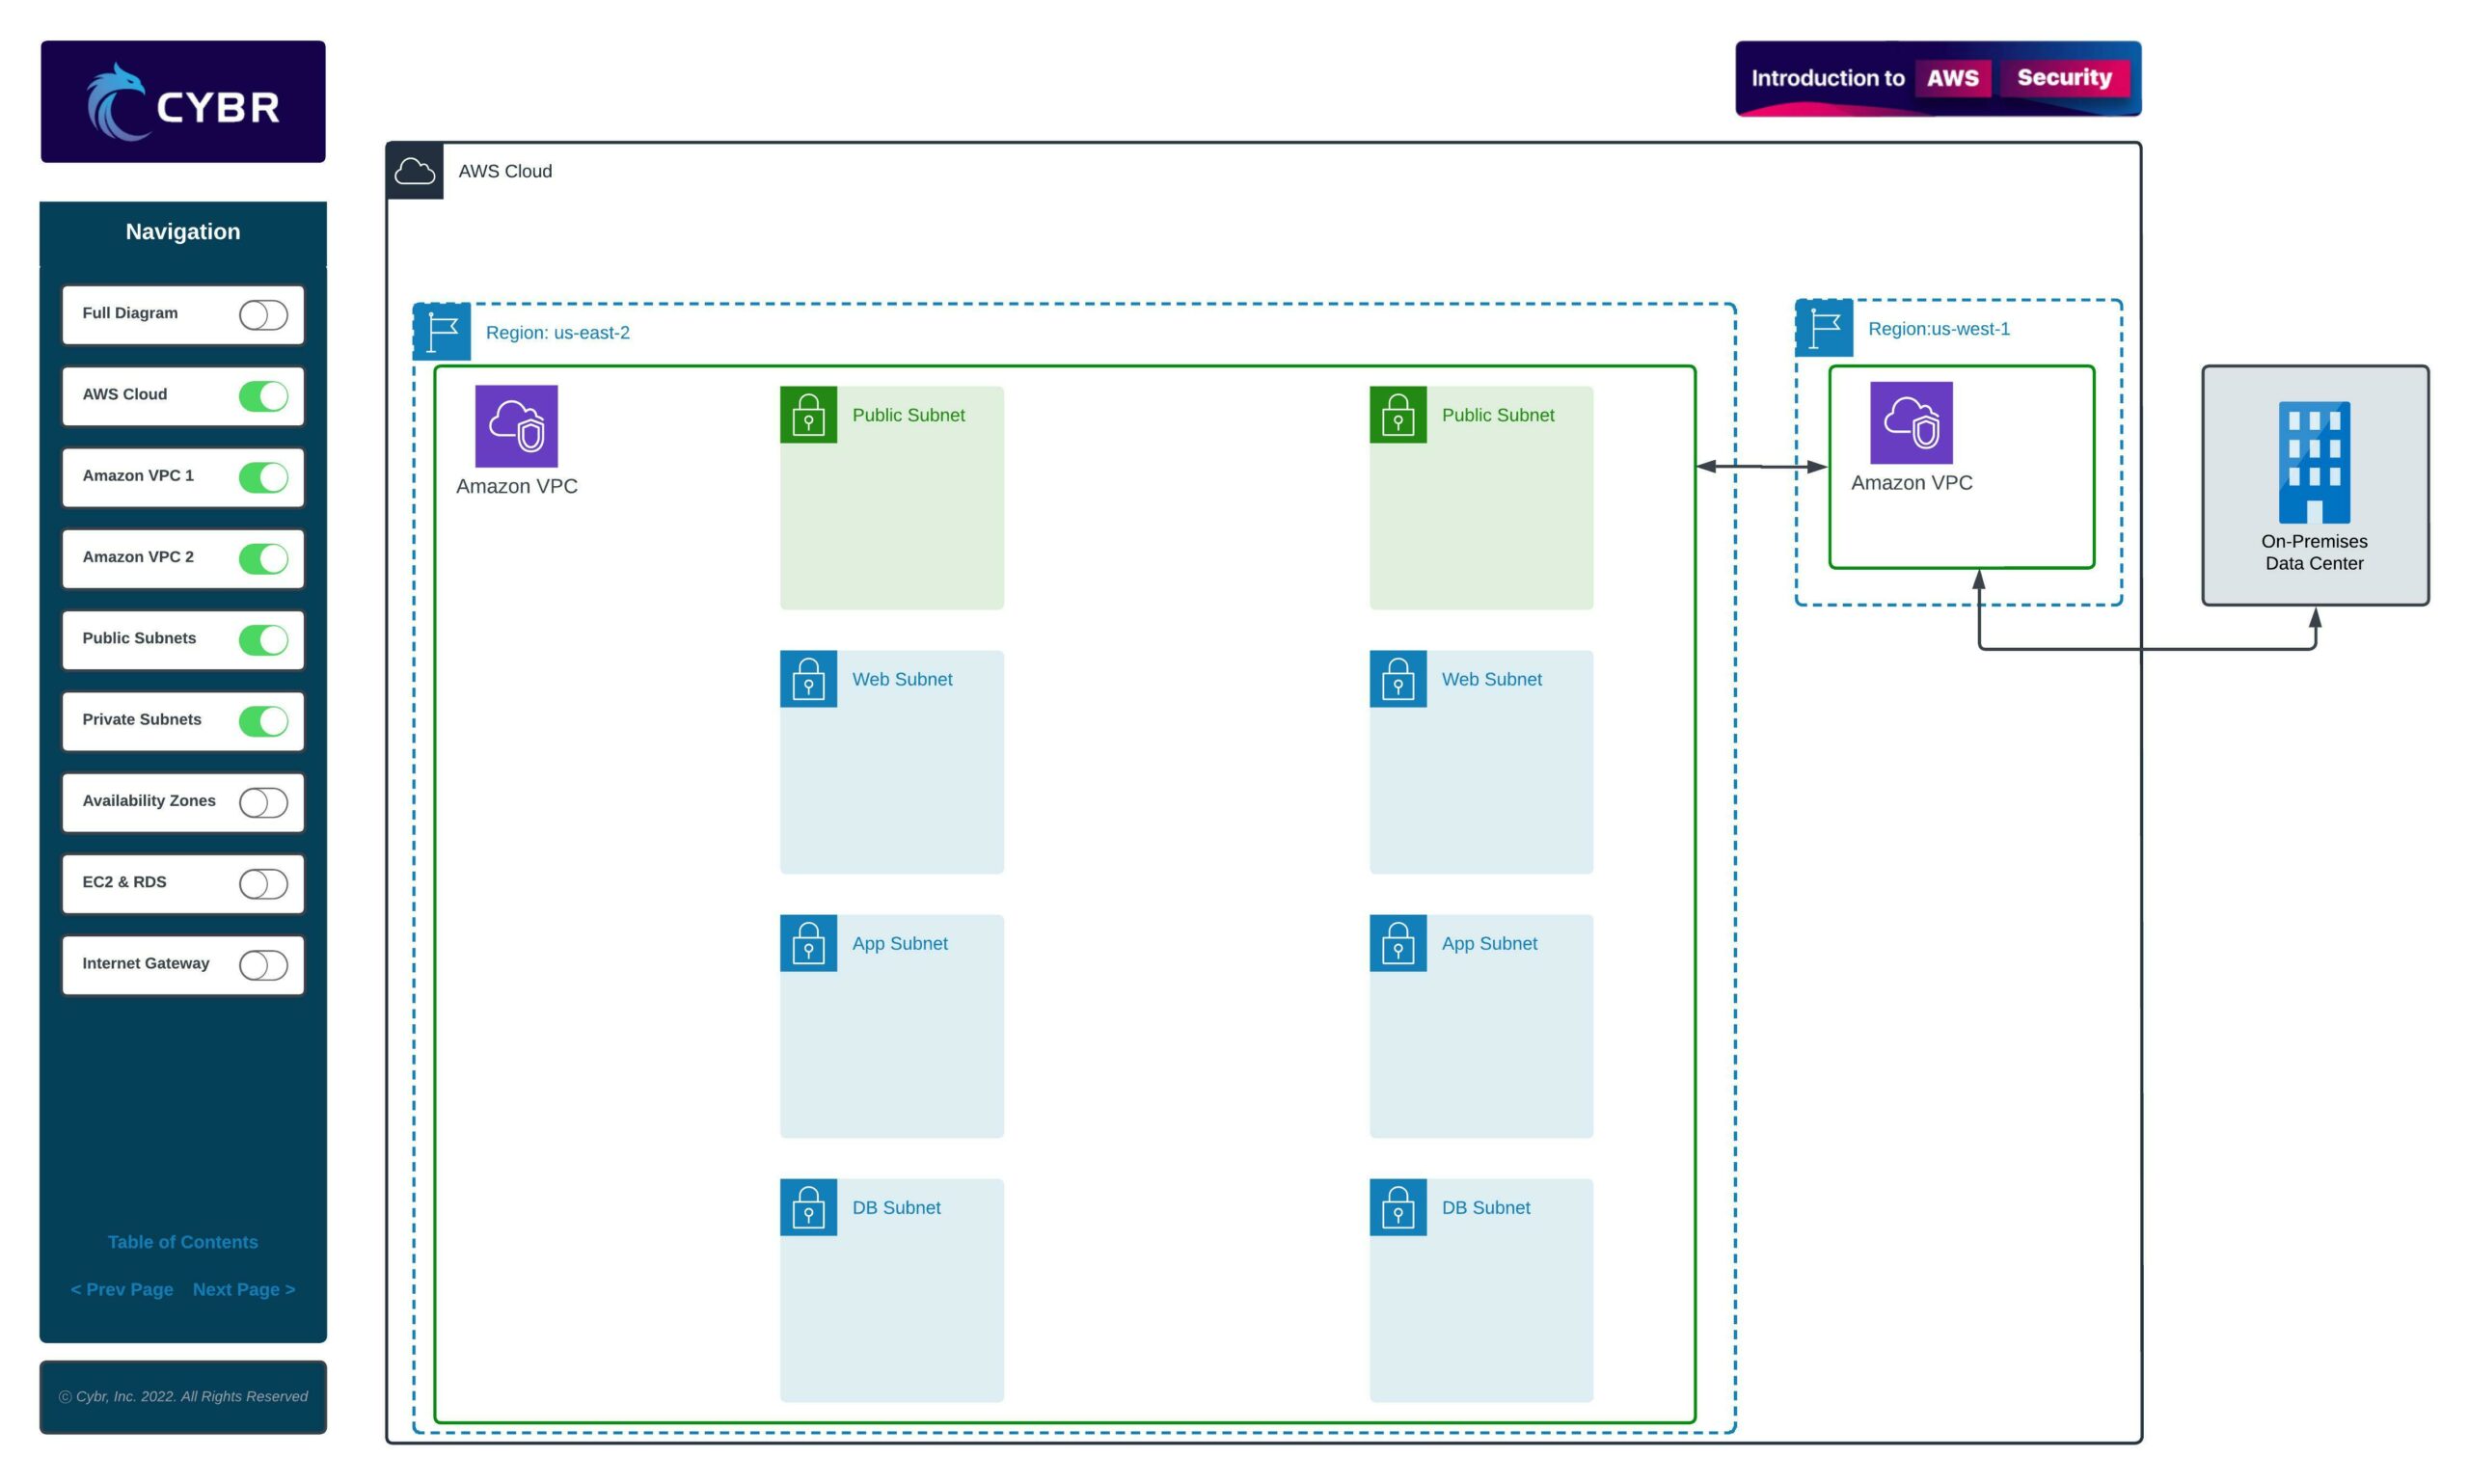
We talked about Regions and Availability Zones in prior lessons. Virtual networks can be created across regions and you can then create subnetworks across zones in order to achieve high availability and data replication.
These subnetworks are more often called subnets, and they further subdivide your virtual network. You can have either public or private subnets, so let’s talk about what that means.
Public and private subnets
Whenever you first create a subnet in a virtual network, that subnet is private by default. Private means that whatever resources you launch within that subnet will only receive a private IP address, and that private IP address won’t resolve from the open Internet. You won’t be able to communicate with that service and that service won’t be able to connect to the Internet without additional configurations.
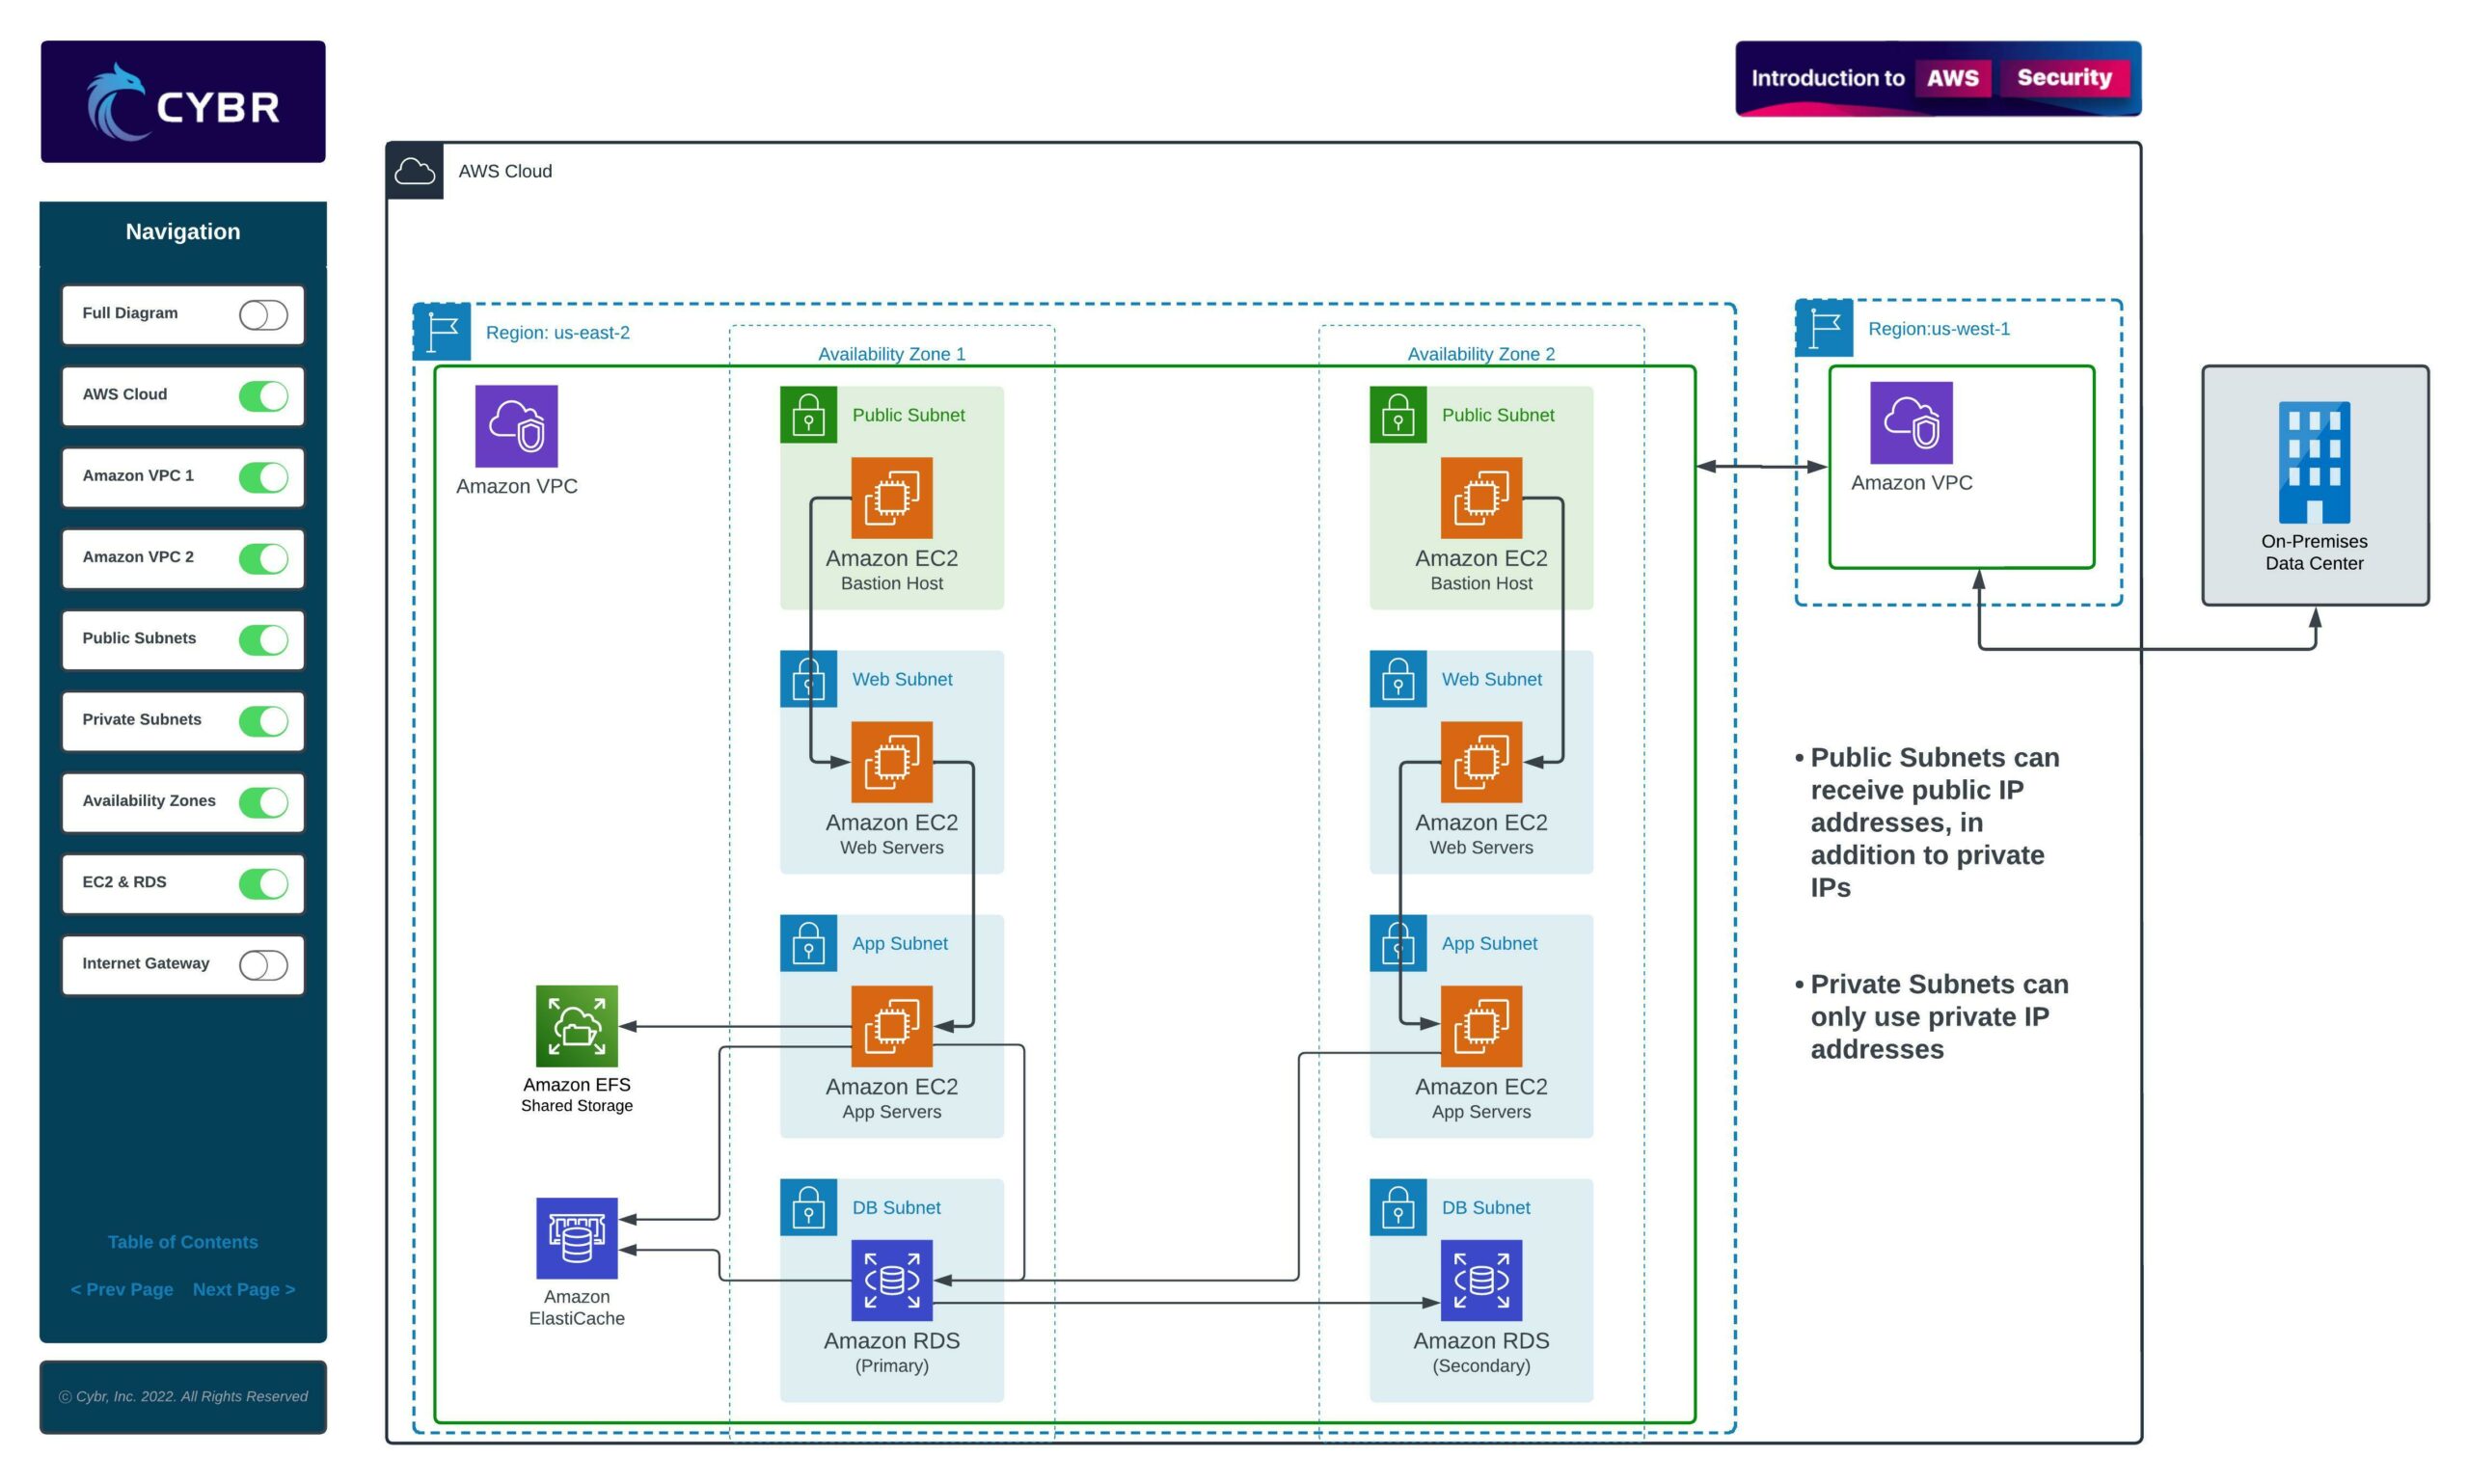
A public subnet, instead, would provide a public IP address to that resource in addition to a private IP address, which means that anyone could access that resource by default.
A subnet becomes public by giving it an Internet Gateway.
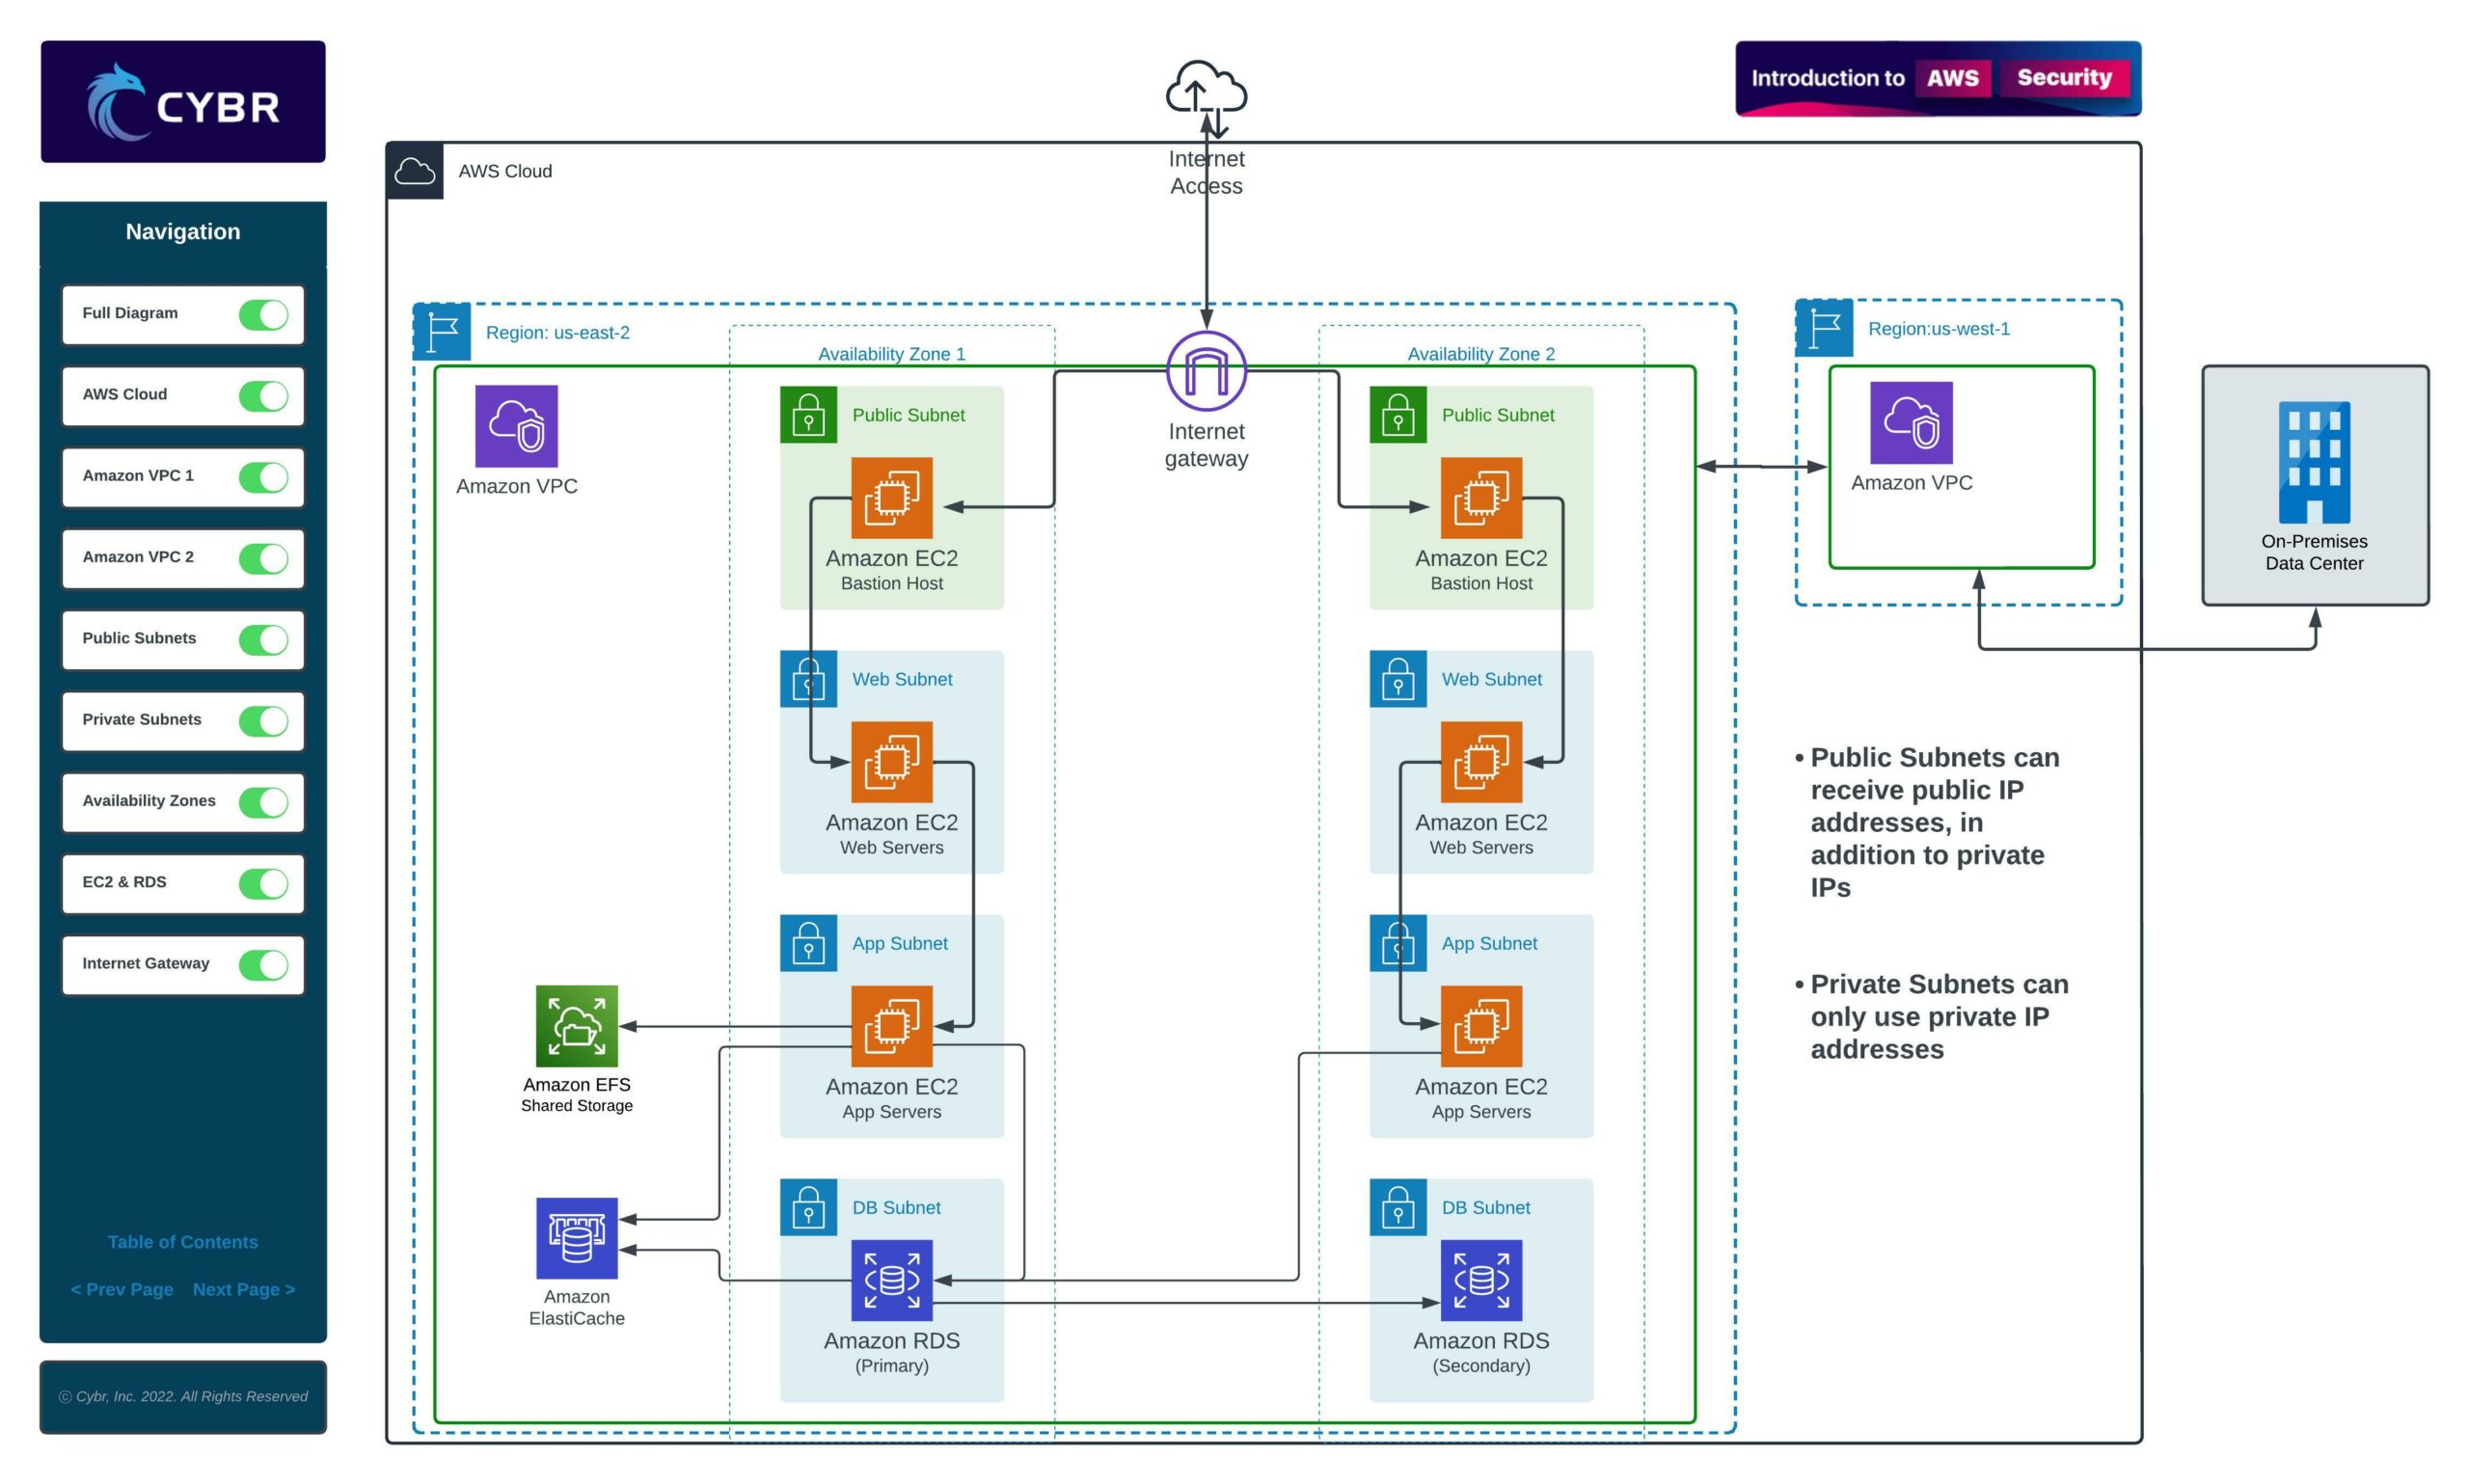
An Internet Gateway creates a door that connects to the Internet so that your virtual network and certain subnets can communicate back and forth with Internet resources. It provides an entry point into your virtual network.
You can think of it in terms of configuring a home network. Before you connect to an Internet Service Provider (ISP) via a modem, you only have a private network that allows you to communicate only with resources within that network, and not the open Internet. Except as soon as you add a modem and pay for your service, plus add a router (if it doesn’t come bundled that way already) those resources within your private network can now access Internet resources.
While it functions differently, the concepts are very similar and this can be a good way for you to remember the difference between public and private subnets.
VPC Security Features
This separation of networks by using public and private subnets is referred to as network segmentation or network isolation, which is an architecture design choice that helps provide a layer of security.
VPCs offer other security features in addition, including:
- Traffic filtering
- Access control
- Capabilities for external connectivity
These security features are going to be the primary focus of this section, but before we can talk about them in more depth, let’s jump into the AWS console to see what a VPC looks like and how we can create one from scratch to fit our needs.
Go ahead and complete this lesson, and we’ll do that in the next!
Comments
Loading comments…