
From the Cybr blog
CompTIA Security+
Read Cybr articles tagged CompTIA Security+.
Browse the archive
Latest articles
Understanding malware classification
Understanding this isn’t required for the CompTIA Security+ exam, meaning that we’re going beyond the scope of this exam for a few minutes, but I…
Read article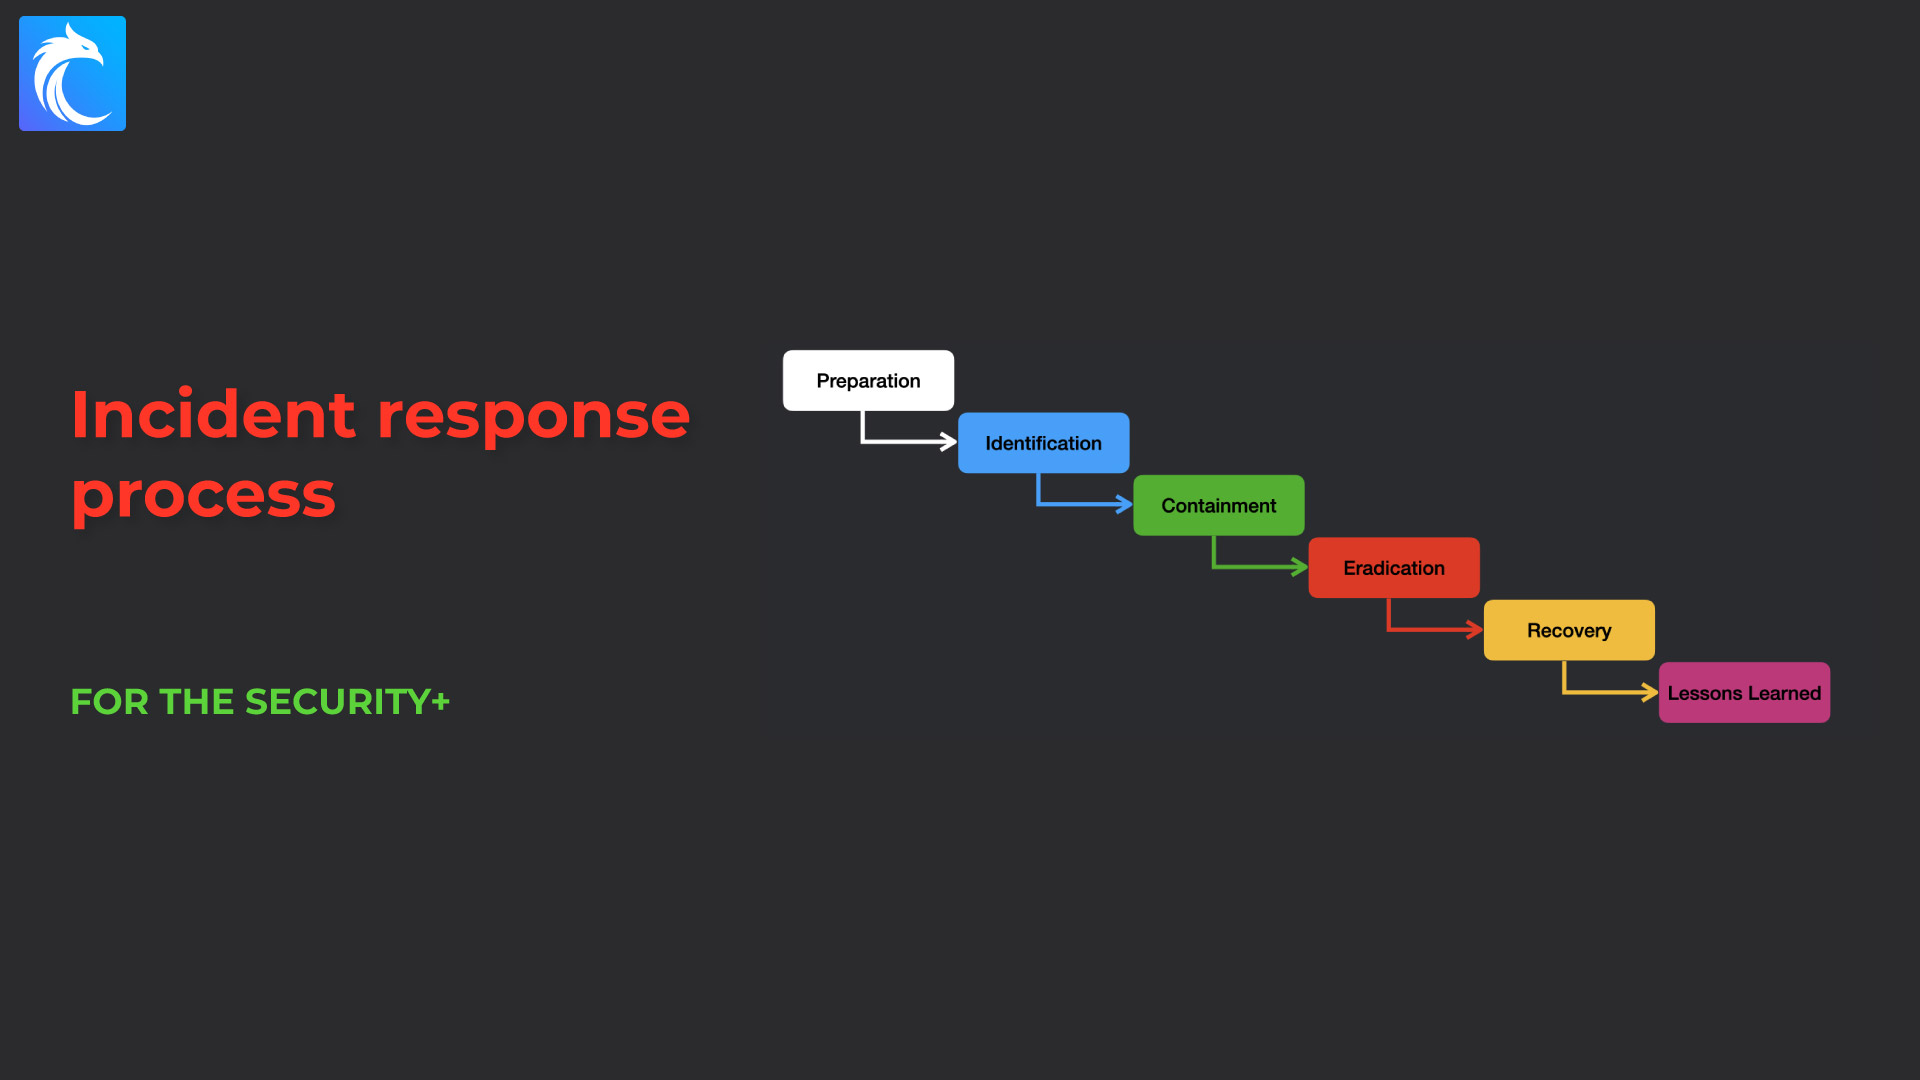
Incident response process
There’s been a security incident in your organization. What do you do? Panic? No ;)! You follow an incident response process. In this article, we’re…
Read articleNetwork Access Control (NAC)
In our course, we talk about Zero Trust and how it’s an approach that believes in continuously checking access and policy violations, even within internal…
Read articleModes of operation
We talked about ciphers and block ciphers in the prior post. A block cipher on its own would only ever encrypt a single block of…
Read articleCipher Suites
When you’re using symmetric encryption you can use what’s known as either a stream cipher or a block cipher. They both ultimately encrypt your data,…
Read articleRequest forgeries (CSRF, XSRF, SSRF)
In 2020, CheckPoint Research announced multiple vulnerabilities in the popular social media application named TikTok. One of the found vulnerabilities allowed an attacker to delete…
Read articleDirectory / Path Traversal
Just like you have directories on your PC, laptop, and mobile phones, web servers also have directories. For example, if you were to purchase web…
Read article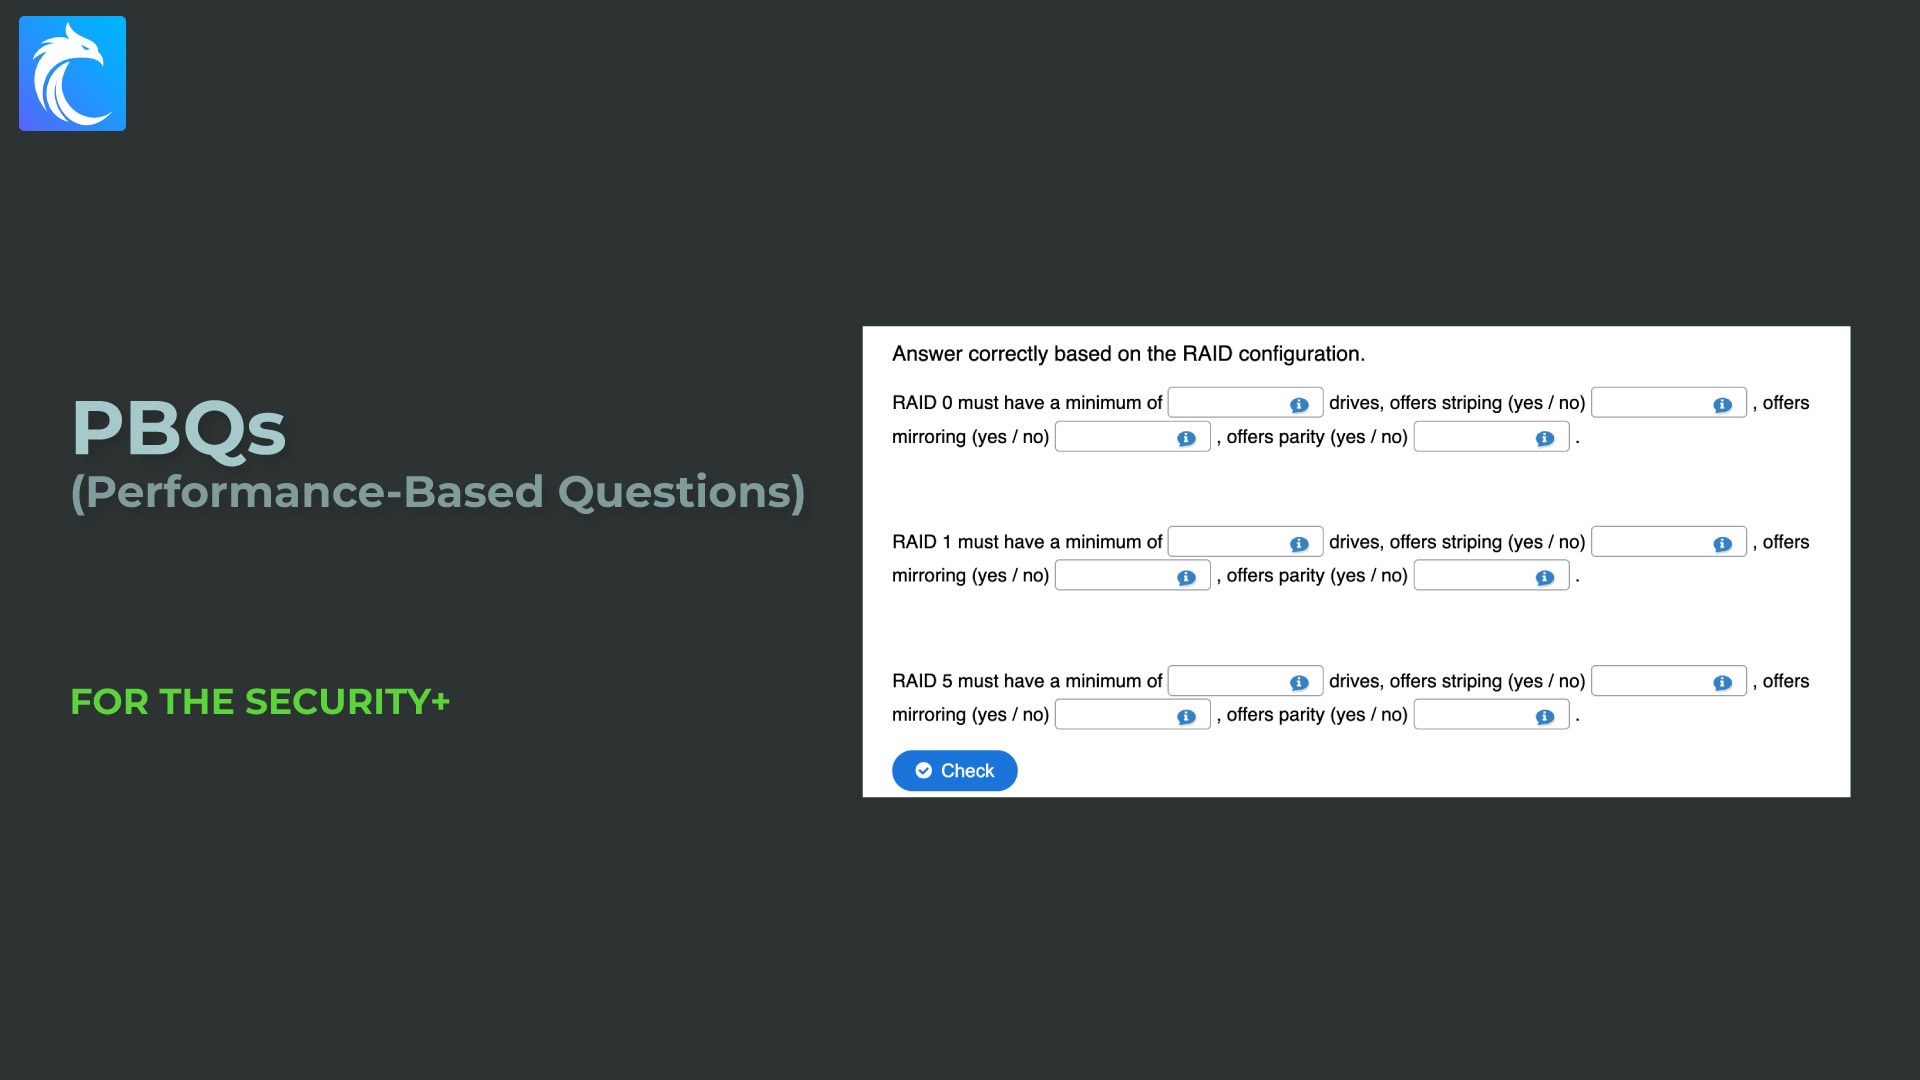
Answers to Performance-Based Questions (PBQs) | Security+ 601
This post contains the answers and explanations to our free Performance-Based Questions (PBQs) that we specifically designed to prepare you to take and pass the…
Read article
Exercise types (red/blue/white/purple teams)
We’ve talked about how we can use vulnerability scans, penetration tests, and bug bounties to find vulnerabilities in our systems. Another approach you may have…
Read articleDisaster Recovery with BCP, COOP, and DRP
For the CompTIA Security+ exam, you need to be familiar with three terms that are related to disaster recovery: What do each of these terms…
Read article