
Premium Hands-on labbeginnerblue teamAWS
Remediate Open SSH Security Groups with AWS Config and SSM
Learn how to configure AWS Config with SSM to detect and automatically remediate open SSH inbound rules in security groups. You will launch an EC2 instance with an overly permissive security group, configure AWS Config, identify the noncompliant resource, and then set up an automated playbook to remediate.
- 9 guided tasks
Scenario
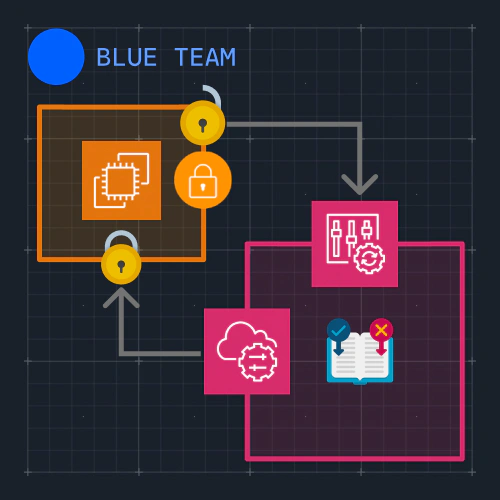
In this lab, we will set up an AWS Config rule to detect security groups that inadequately restrict SSH port 22, leaving it open to the entire world with 0.0.0.0/0, a practice that should rarely, if ever, be used. We will then configure an automated remediation playbook with AWS Systems Manager (SSM) to automatically address noncompliant resources, removing the noncompliant inbound rule.
What you will learn
- Create an AWS Config rule to detect unrestricted SSH access.
- Launch an EC2 instance with an open SSH security group.
- Configure SSM automatic remediation for noncompliant security groups.
- Verify that remediation removes the open SSH rule.
Hands-on lab
Remediate Open SSH Security Groups with AWS Config and SSM
Included in Cybr Premium.