
From the blog
Blog
Read practical cloud security, application security, and cybersecurity guides, tutorials, and research from Cybr.
Browse the archive
More Blog articles
IaC Scanning and Policy as Code with Checkov [Cheat Sheet]
We posted a video introducing the benefits of Infrastructure as Code (IaC) scanning and Policy as Code scanning, and why you absolutely should be running…
Read articleDirectory / Path Traversal
Just like you have directories on your PC, laptop, and mobile phones, web servers also have directories. For example, if you were to purchase web…
Read article
HashiCorp Vault [Cheat Sheet]
We wrote a blog post introducing and explaining what Vault is, when it’s useful, and how to get started using it to manage your secrets.…
Read article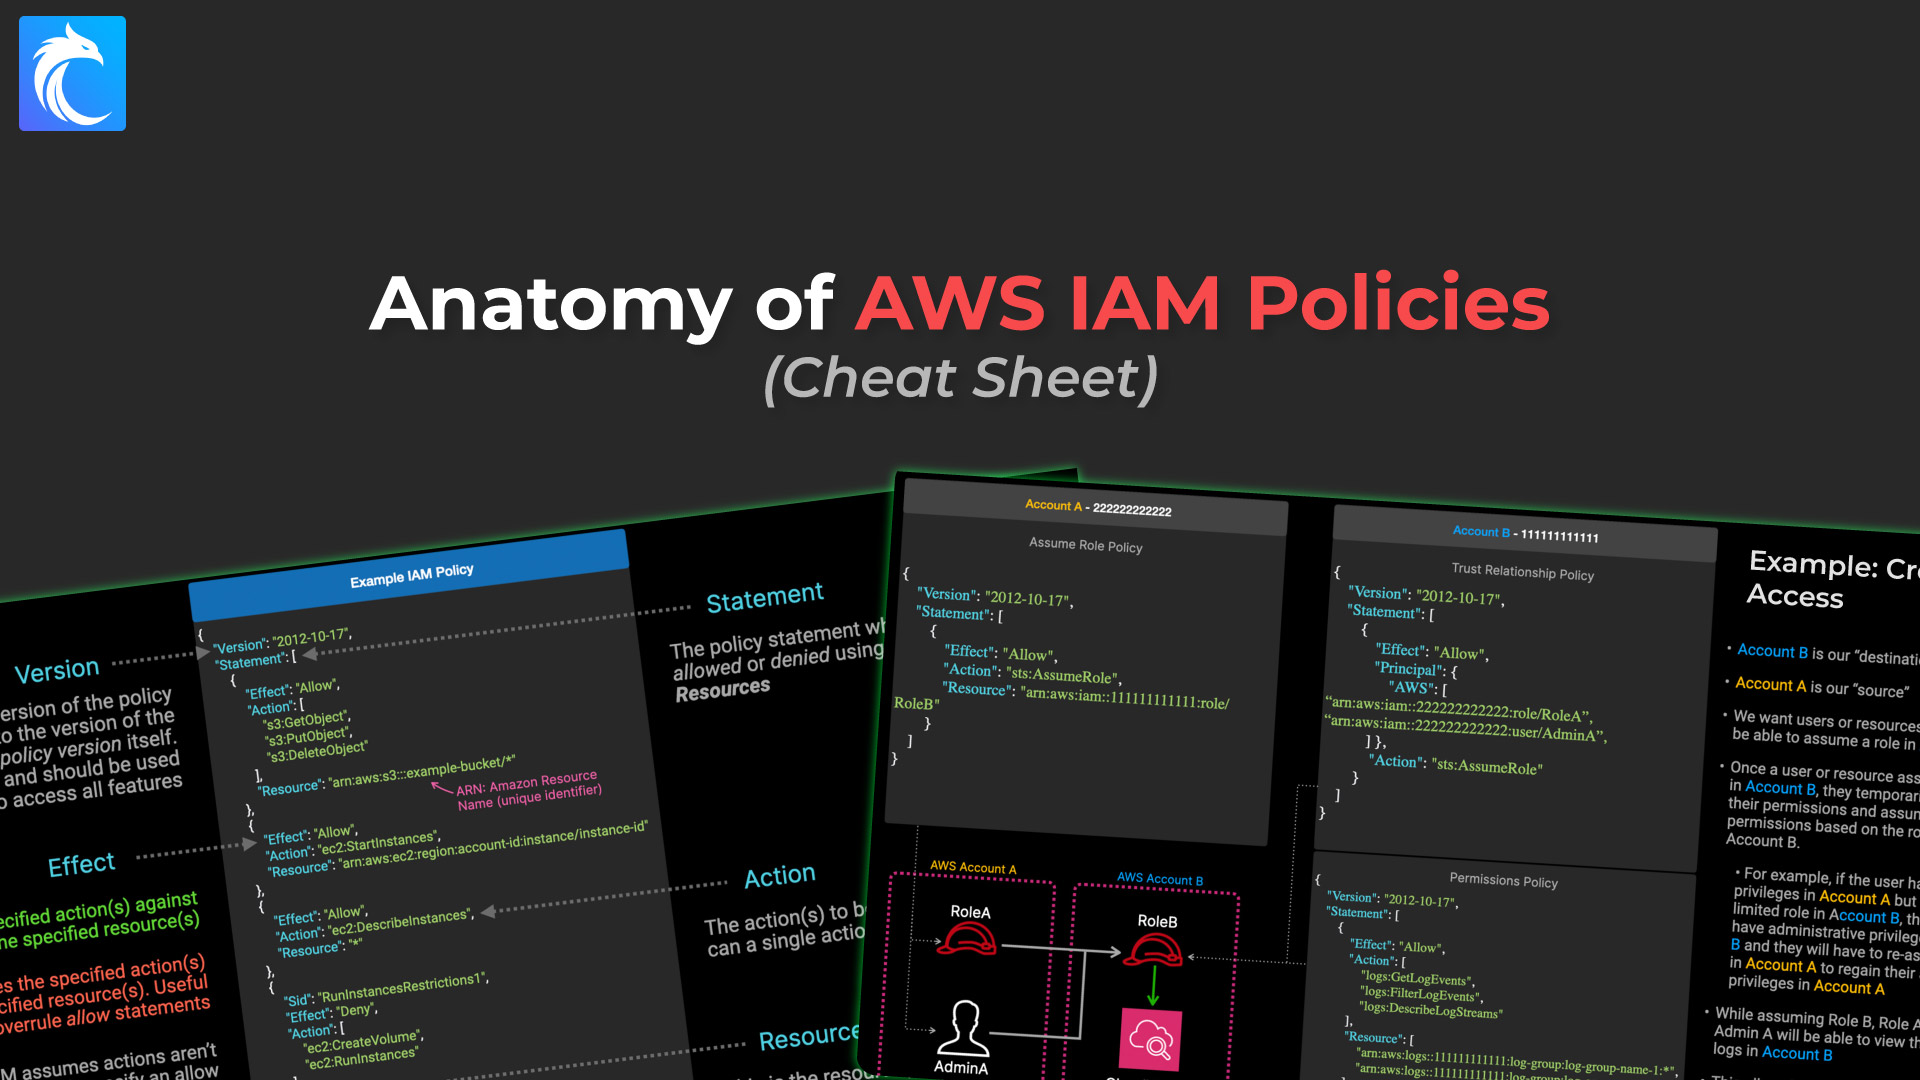
Anatomy of an AWS IAM Policy [Cheat Sheet]
If we had to name the most critical service to understand when it comes to AWS security, it would have to be IAM (Identity and…
Read article
How crypto miners hijack AWS accounts (Cryptojacking GUI-Vil Case Study)
This is the story of how you print free money. It’s a story that involves an AWS account, a threat actor named GUI-Vil, and unauthorized…
Read article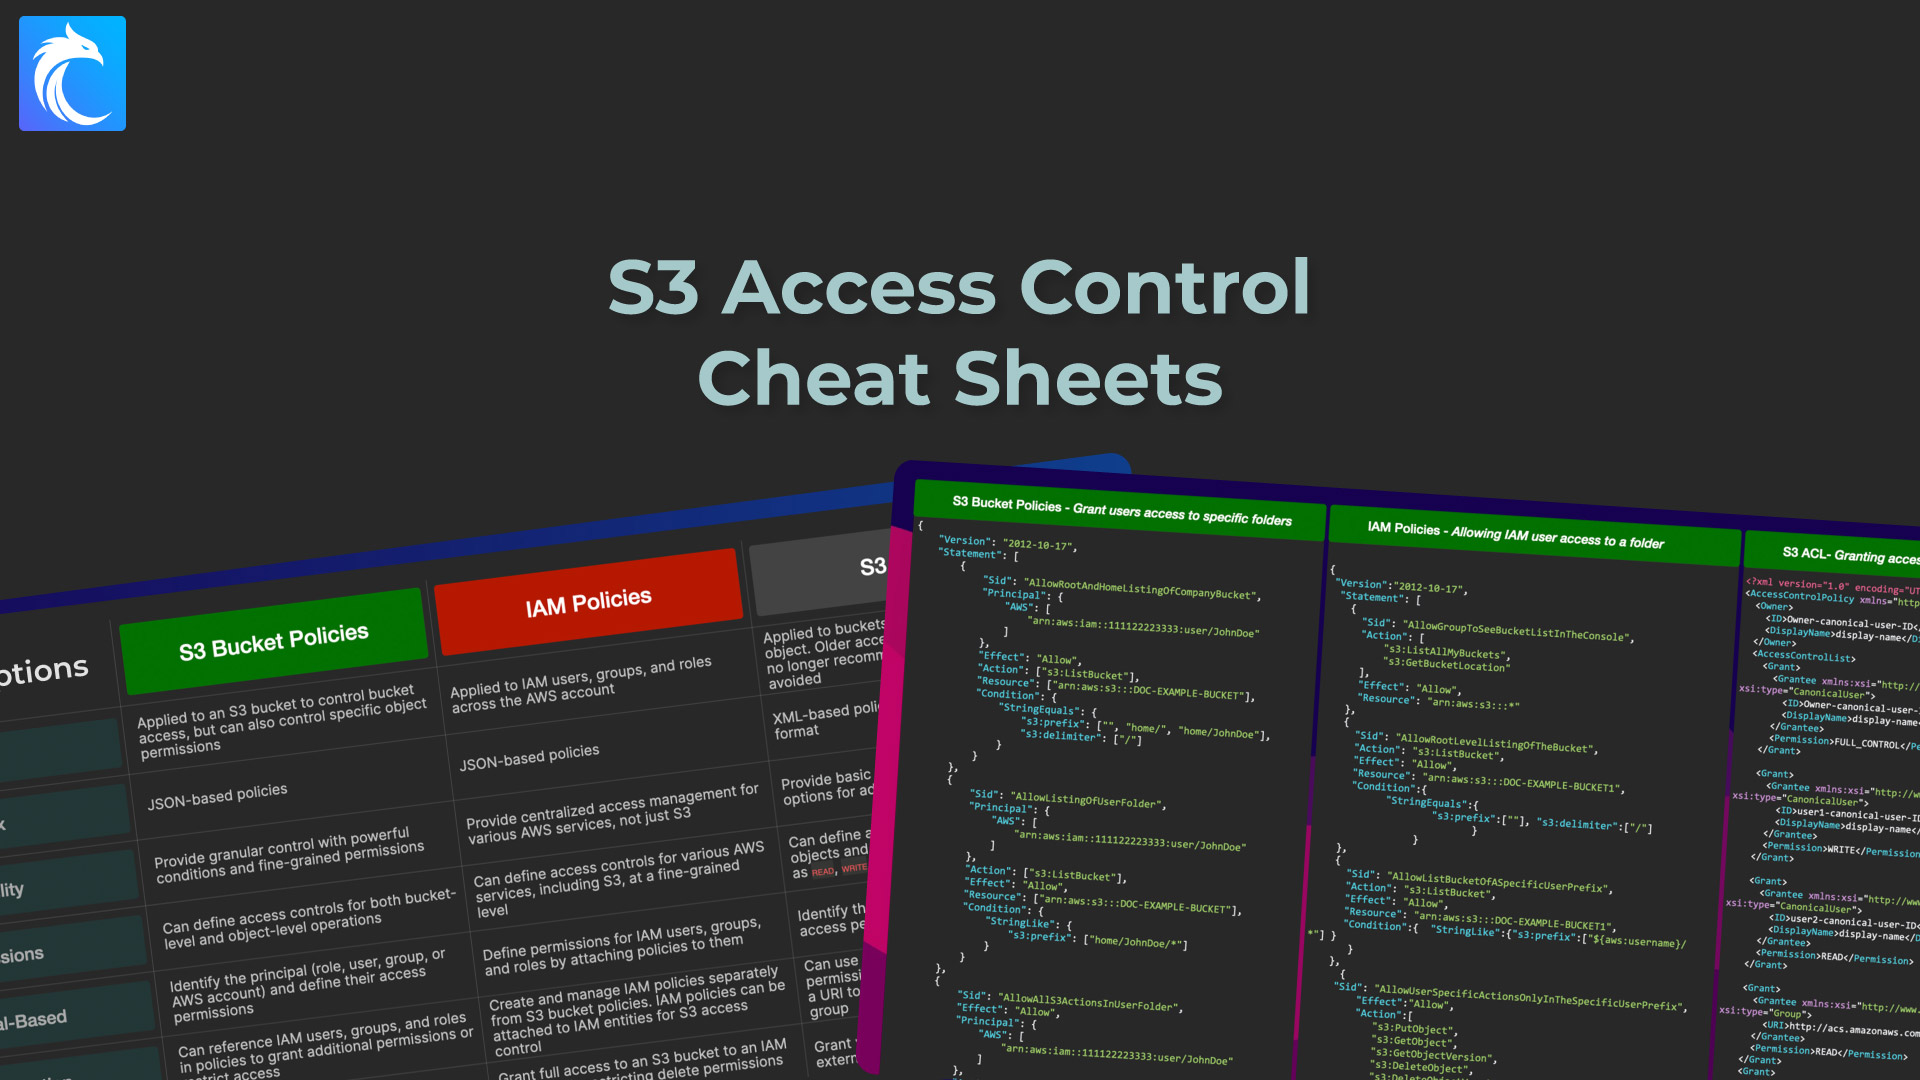
S3 Bucket Policies vs. ACLs vs. IAM Policies [Cheat Sheet]
Understanding when to use S3 Bucket Policies versus S3 ACLs versus AWS IAM Policies can easily make your head spin. To make sense of it,…
Read article
Intro to AWS Pentesting (with Pacu)
In this article, you’re going to learn how to hack AWS cloud environments so that you can find exploitable vulnerabilities in your own AWS accounts…
Read article
Answers to Performance-Based Questions (PBQs) | Security+ 601
This post contains the answers and explanations to our free Performance-Based Questions (PBQs) that we specifically designed to prepare you to take and pass the…
Read articleStatic Application Security Testing (SAST)
What if you could take multiple senior developers and security experts, distill them into a tool, and then have the ability to run that tool…
Read article
Exercise types (red/blue/white/purple teams)
We’ve talked about how we can use vulnerability scans, penetration tests, and bug bounties to find vulnerabilities in our systems. Another approach you may have…
Read article