
From the Cybr blog
OWASP Top 10
Read Cybr articles tagged OWASP Top 10.
Browse the archive
Latest articles
Request forgeries (CSRF, XSRF, SSRF)
In 2020, CheckPoint Research announced multiple vulnerabilities in the popular social media application named TikTok. One of the found vulnerabilities allowed an attacker to delete…
Read articleDirectory / Path Traversal
Just like you have directories on your PC, laptop, and mobile phones, web servers also have directories. For example, if you were to purchase web…
Read articleStatic Application Security Testing (SAST)
What if you could take multiple senior developers and security experts, distill them into a tool, and then have the ability to run that tool…
Read articleWhat are SQL Injections? // Explained in 180 seconds
Whenever you visit a website or use some kind of application, that website or app needs to pull data from a database. For example, let’s…
Read article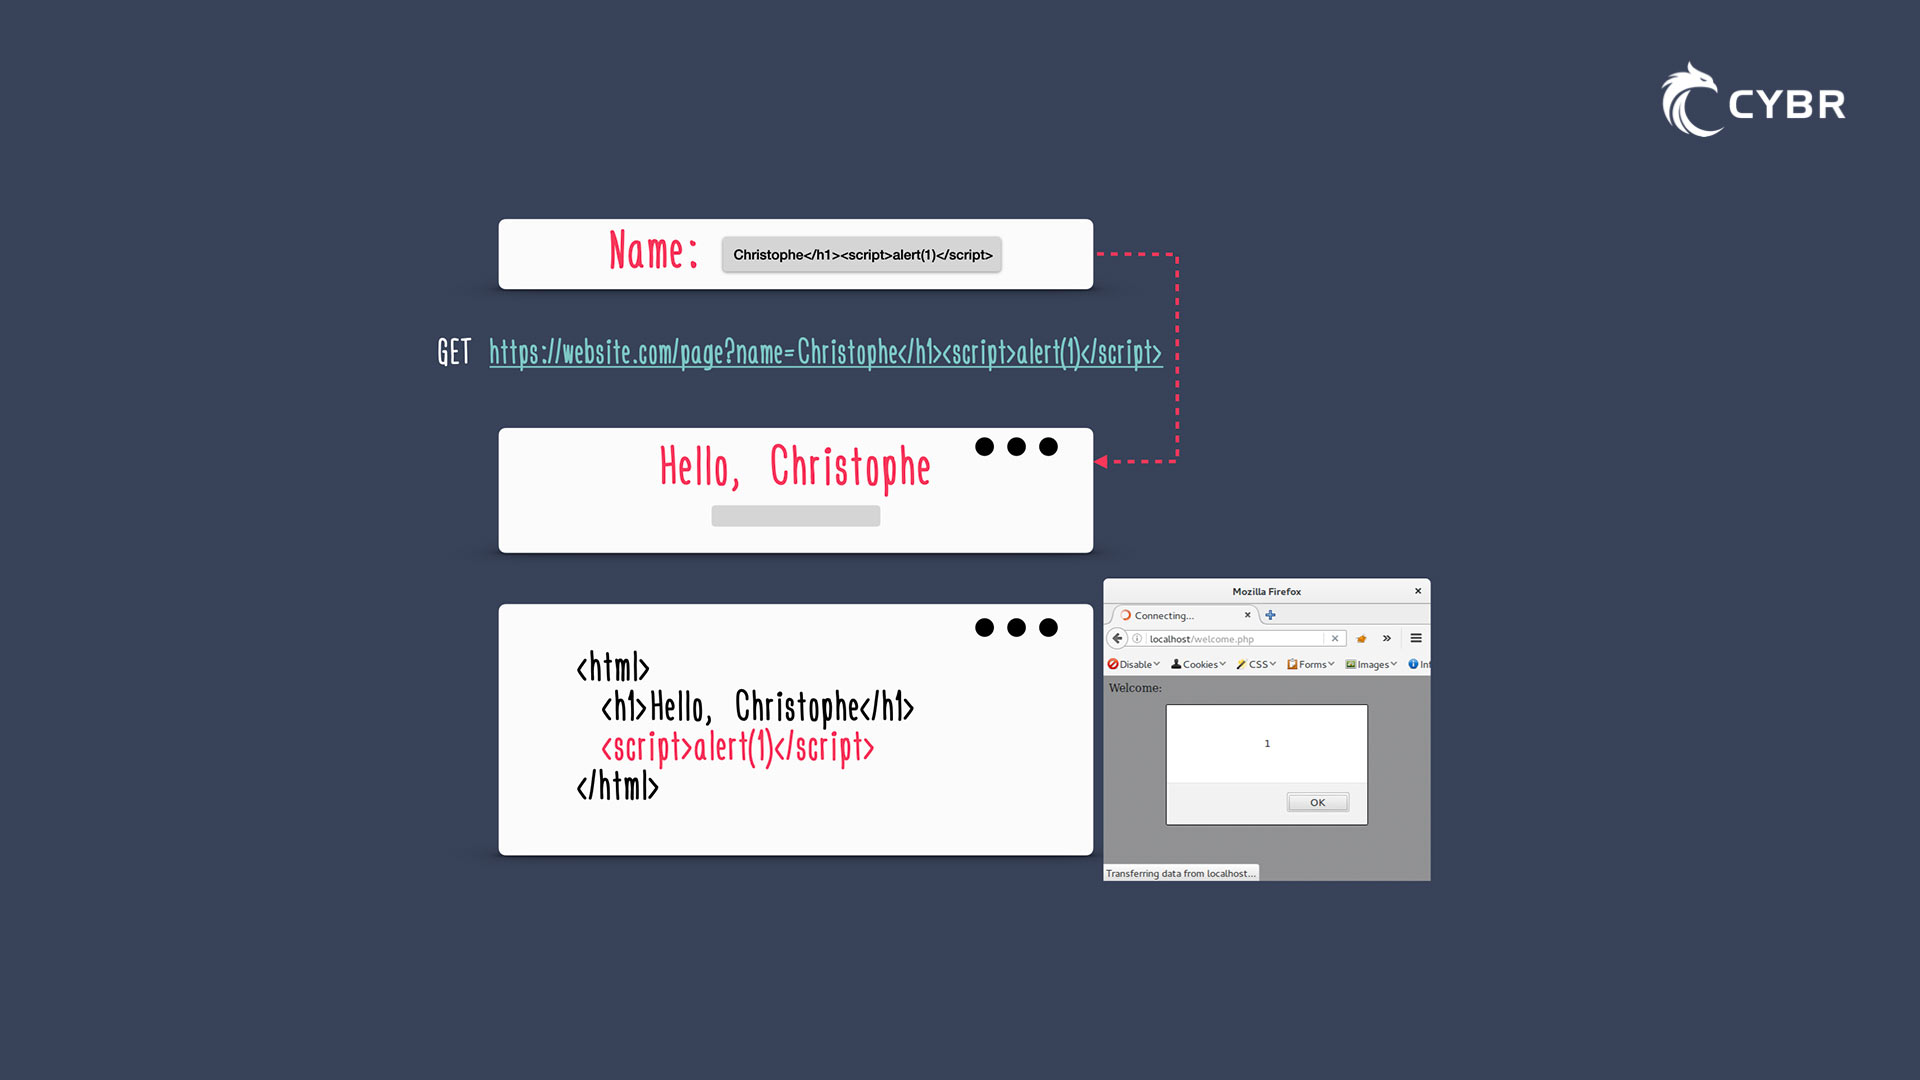
What is Cross-Site Scripting (XSS)?
According to both OWASP and CWE, Cross-Site Scripting is one of the top 10 most dangerous web application security risks, and for good reason: OWASP’s…
Read article
4 steps to getting started securing applications
A lot of times, especially when you join smaller organizations, there are no (or very few) formal processes in place. The approach taken to secure…
Read article
Uploading Backdoor Shells with Weevely and Commix
Now that we’ve reviewed OS Command injection concepts like how they work, the impact they can have, and techniques that can be used to exploit…
Read article
Set up the OWASP Juice Shop on Kali with Docker [Quickest Method]
Installing the OWASP Juice Shop on Kali with Docker is super fast because you don’t have to install anything but Docker. It also makes cleaning…
Read article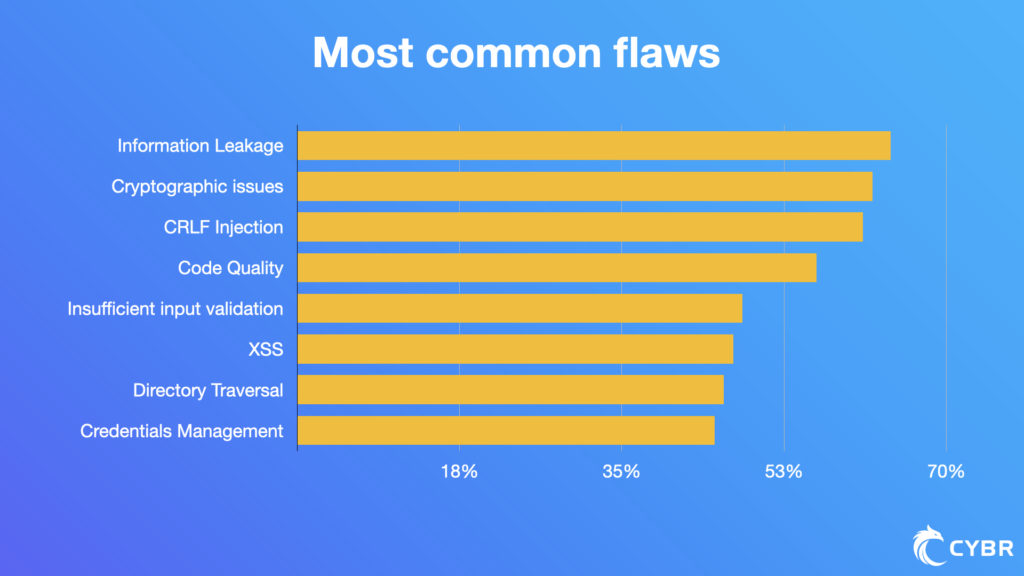
What is Information Leakage, and how do you prevent it?
One of the most commonly found flaws in web applications and mobile applications is information leakage. But what is information leakage, why is it a…
Read articleThe 3 Most Common Mobile Application Security Risks
Considering our reliance on mobile applications for our day-to-day personal and professional lives, mobile application security should be taken seriously, but unfortunately isn’t always. Especially…
Read article